 ProMapRanker
Best GRC Compliance Platforms in 2026

Key takeaways
- Vanta and Drata lead for startups and midsize SaaS teams that need SOC 2 or ISO 27001 quickly.
- Secureframe and Sprinto suit teams that want guided help and clearer entry pricing.
- Hyperproof, AuditBoard, OneTrust, and LogicGate suit larger programs with wider risk and audit needs.
- Most platforms use custom or tiered pricing, so budget for the platform, the audit, and any per-framework fees together.
Quick comparison
| Pick | Great for | Pricing starts at | Free tier | |
|---|---|---|---|---|
 Vanta | Broad frameworks and wide auditor choice | See website | No | Visit |
 Drata | Engineering-led teams with custom tooling | See website | No | Visit |
 Secureframe | Guided compliance with named support | See website | Free trial | Visit |
 Sprinto | First audit with guided help | See website | No | Visit |
 Hyperproof | Multi-framework programs at renewal scale | See website | No | Visit |
 AuditBoard | Enterprise risk, audit, and controls programs | See website | No | Visit |
 OneTrust | Privacy, risk, and governance at enterprise scale | See website | No | Visit |
 LogicGate | Flexible risk workflows and control tracking | See website | No | Visit |
The best grc compliance platforms
We compared framework coverage, evidence automation, integrations, auditor support, and pricing transparency, using vendor pages and public pricing guides. GRC here means governance, risk, and compliance in one program, not just a single-framework checklist tool.
Vanta is the most common first pick for SaaS companies that need SOC 2 to close enterprise deals. It connects to cloud and SaaS tools, runs automated checks on controls, collects evidence, and gives auditors a structured workspace. The framework library covers SOC 2, ISO 27001, HIPAA, and other common standards.
The cost needs careful reading. Platform pricing is typically custom and tiered, and each added framework can raise the bill. The audit fee is separate, paid to an independent firm. For a team that needs one framework fast and values auditor choice, Vanta is a strong default. For a team on a tight budget, compare the full first-year total, not just the platform quote.
- Many integrations and automated control tests
- Wide framework library
- Large auditor partner network
- Custom pricing that rises with frameworks
- Audit itself is billed separately
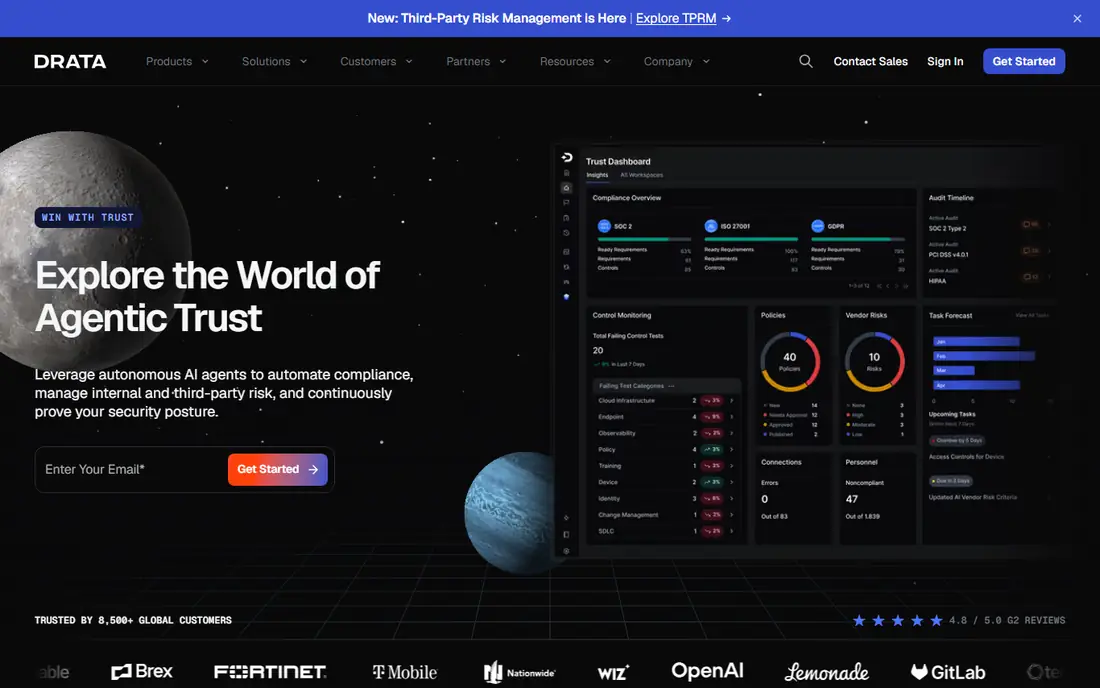
Drata appeals to engineering-heavy teams that want compliance to feel like part of their stack. It monitors controls daily, connects to many developer and cloud tools, and supports testing controls as code in some workflows. That approach suits teams that already automate infrastructure and want evidence to follow the same pattern.
Pricing is custom, and the total depends on company size and frameworks. Smaller teams should ask what is included at the entry tier and what counts as an add-on. For midsize teams planning several frameworks, Drata pricing can compare well with rivals, especially when user counts grow.
- Strong integrations and daily control monitoring
- Controls testing suited to engineering teams
- Large auditor network
- Custom pricing
- Custom frameworks can cost extra
Secureframe suits growth-stage teams that want a person to guide them, not just software. It automates evidence collection, drafts policies, and monitors controls, while compliance managers help plan the audit path. That support matters for teams without a dedicated compliance lead.
The entry tier is more limited than higher tiers, especially for custom tests and advanced features. Teams should check which frameworks and support levels are included before signing. For a first multi-framework program, the guided model can save weeks of guesswork.
- Guided onboarding and compliance managers on higher tiers
- Many integrations
- Federal framework support
- Audit billed separately
- Entry tier limits some custom tests
Sprinto is built for companies doing their first audit. The onboarding walks teams through controls, evidence, and policies in order, rather than leaving them to map a framework alone. Integrations cover common cloud, HR, and ticketing tools, and device monitoring checks endpoint controls.
Lower tiers limit some AI questionnaire features, so teams with heavy vendor security questionnaires should check that allowance. Pricing varies with frameworks and headcount, so request a quote for your exact scope. For a small team that wants structure and support, Sprinto is a practical choice.
- Guided setup for first-time teams
- Many integrations and device monitoring
- Auditor network support
- AI questionnaire limits on lower tiers
- Pricing varies by framework and size
Hyperproof fits companies that already run compliance and need to manage it year after year. Its strength is control mapping, where one piece of evidence supports several frameworks at once. That reduces duplicate work when a company adds ISO 27001 on top of SOC 2, or adds a privacy framework later.
It is less of a guided first-audit product than Vanta or Secureframe. Teams should expect a more program-led setup and a sales conversation for pricing. For a mature program with several frameworks and an internal compliance owner, Hyperproof offers control and reuse that simpler tools lack.
- Maps one control to many frameworks
- Structured audit workspace
- Suited to ongoing programs
- No published pricing
- Less of a first-audit hand-holding tool
AuditBoard serves larger companies that run risk management, internal audit, and compliance as one connected program. It offers modules for risk registers, audit planning, controls testing, and reporting, with dashboards for leadership. That breadth suits regulated companies and public companies with formal audit functions.
Small teams will find it heavy and expensive. Implementation takes planning, and the value appears when many teams and auditors work in the same system. For an enterprise that needs audit and risk in one platform, AuditBoard is a serious contender.
- Wide risk, audit, and controls modules
- Strong reporting for boards and executives
- Suited to large teams
- Enterprise pricing and implementation
- More than a small team needs
OneTrust is best known for privacy, but its platform also covers risk, third-party management, and governance workflows. Companies with global privacy duties, many vendors, and complex data flows use it to keep privacy and risk work in one place. That scope helps when privacy, security, and legal teams must share evidence.
The breadth is also the drawback. Setup and configuration take time, and smaller teams may use only a small part of the platform. For a company where privacy is a core risk, OneTrust is worth evaluating. For a startup that only needs SOC 2, a focused compliance tool will move faster.
- Broad privacy and governance modules
- Strong for global privacy rules
- Enterprise integrations
- Broad scope can mean complex setup
- Pricing is custom
LogicGate suits teams that want to design their own risk and compliance workflows rather than follow a fixed template. Its no-code builder lets teams map controls, assign owners, track issues, and build reports that match internal processes. That flexibility helps companies with unusual structures or regulated workflows.
Flexibility needs ownership. Without a clear internal owner, a flexible tool can become a set of half-built workflows. Pricing is custom, so scope the modules you need before requesting a quote. For a team with a defined risk process and an owner to run it, LogicGate is a strong fit.
- Flexible no-code workflows for risk and controls
- Good for custom processes
- Reporting and dashboards
- Custom pricing
- Needs an internal owner to design workflows
How we picked these
We compared official vendor pages, framework lists, integration counts, and public pricing guides, and we kept only platforms that were still sold in October 2026. We looked at evidence automation, auditor support, multi-framework mapping, risk features, and pricing transparency. Each pick had to support a real GRC program, not just a single checklist or document template.
How to choose a GRC compliance platform
Start with the framework your customers actually ask for. SOC 2 is the common first ask for SaaS, ISO 27001 is common for international buyers, and HIPAA or PCI DSS apply to specific industries. Next, count the total cost. Platform fees, per-framework fees, audit fees, penetration testing, and internal staff time all belong in the same budget.
Check integrations against your real stack. A platform that connects to your cloud, identity, HR, and ticketing tools will automate far more evidence than one that needs manual uploads. Finally, ask about auditor fit. Some platforms work with many audit firms, while others bundle an in-house firm or a partner network. Auditor choice affects timeline and cost, so confirm it early.
First audit versus mature program
First-time teams need guidance, templates, and a clear path to audit readiness. Mature teams need control reuse, reporting, and workflow flexibility across many frameworks. Buying a mature enterprise platform for a first audit often slows you down, while buying a first-audit tool for a large program can force a painful migration later.
Vendor risk and questionnaires
Many GRC platforms also help with vendor risk and security questionnaires. If your team answers dozens of customer questionnaires a year, check questionnaire automation limits and AI features. A platform that only tracks your own controls will leave that workload untouched.
Frequently asked questions
What is the best GRC compliance platform for SOC 2?
Vanta, Drata, and Secureframe are the most common SOC 2 choices for SaaS teams. Vanta offers broad auditor choice, Drata suits engineering-led teams, and Secureframe offers guided support. The best pick depends on team size, stack, and how much guidance you need for a first audit.
What are the best GRC compliance tools for small businesses?
Sprinto and Secureframe suit smaller teams doing a first audit, because they offer guided setup and clearer entry paths. Vanta also works for small SaaS teams that need SOC 2 quickly. Compare full first-year costs, including audit fees, before you choose on platform price alone.
How much do GRC compliance platforms cost?
Entry costs vary widely, and many vendors use custom pricing. Small-team platform fees often start in the low five figures per year, and audits are billed separately. Always request a quote for your company size and framework list, and ask what counts as an add-on.
What is the difference between GRC software and compliance automation?
Compliance automation focuses on evidence collection and audit readiness for a specific framework. GRC software covers a wider program, including risk registers, internal audit, controls, and governance workflows. Many modern platforms do both, but enterprise GRC tools offer deeper risk and audit modules.
Do GRC platforms include the audit itself?
Usually no. The platform prepares evidence and controls, while an independent audit firm tests them and issues the report. Some vendors bundle audit services through a partner or an in-house firm, but that fee is normally separate from the platform subscription. Confirm the audit model before you sign.
How long does a first SOC 2 audit take with a GRC platform?
A Type 1 report can be ready within weeks to a few months on a clean stack, while a Type 2 report needs an observation period, commonly three to twelve months. The platform speeds up readiness, but it cannot shorten the observation window an auditor requires. Plan the timeline with your auditor, not just the vendor.
Sources
See where you really rank - block by block
ProMapRanker scans Google Maps across a grid of your service area. Simple monthly plans from $19, white-label on every plan.
Start freeKeep reading
 best virtual meeting platform
Best Virtual Meeting Platforms in 2026
Searching for the best virtual meeting platform? We compare 9 video meeting tools on price, free plans, capacity, and features for teams of all sizes.
Read → best social media reporting tools
Best Social Media Reporting Tools in 2026
Compare the best social media reporting tools in 2026, with pricing and free plans, and the right pick for creators, agencies, and large marketing teams.
Read → best social media platforms for business
Best Social Media Platforms for Business in 2026
We compared the best social media platforms for business, from Facebook and Instagram to LinkedIn and TikTok, with ad strengths and who each platform suits.
Read →