 ProMapRanker
6 Best Vulnerability Scanning Software for Web Agencies for 2026

Practical web application security testing · Pricing starts at: See website
Direct answer
Burp Suite comes first here, mainly for practical web application security testing. Listed starting prices: Detectify from €2,500 annual platform fee and Invicti from $500 per pentest. For a different need, Acunetix covers end-to-end web security scanning and Rapid7 InsightVM covers vulnerability management with exposure context. The full list of 6 tools follows, with prices and free plan facts.
ProMapRanker put together this guide to vulnerability scanning software for web agencies for readers who want a clear shortlist without reading every vendor page. It compares 6 tools on starting price, free plans, who each one suits and where each one falls short.
Key takeaways
- This list starts with Burp Suite, which is built for practical web application security testing.
- Only Detectify offers a free plan among these 6 tools.
- The main caution on Rapid7 InsightVM: positioned within a broader system.
- Expect to ask for a quote from Burp Suite, Acunetix, Rapid7 InsightVM and Tenable Nessus; the other tools show a starting price.
- Tenable Nessus fits wide network and host vulnerability assessment.
Quick comparison
| Pick | Great for | Pricing starts at | Free tier | |
|---|---|---|---|---|
| Burp Suite | Practical web application security testing | See website | Not stated | Visit |
 Acunetix | End-to-end web security scanning | See website | Not stated | Visit |
 Rapid7 InsightVM | Vulnerability management with exposure context | See website | Not stated | Visit |
 Detectify | External exposure checks with hacker-driven research | €2,500 annual platform fee | Yes | Visit |
 Invicti | Automatic web application and API security testing | $500 per pentest | Not stated | Visit |
 Tenable Nessus | Wide network and host vulnerability assessment | See website | Not stated | Visit |
The full vulnerability scanning software for web agencies list
Burp Suite was built for practical web application security testing. The vendor gives you a set of security tools for identifying vulnerabilities.
Where it is weaker: Less suited to unattended fleet scanning.
Burp Suite rewards practical skill, so results depend heavily on the tester. It is less of a set-and-forget scanner for checking dozens of client sites automatically. Check the vendor site for Burp Suite pricing; none is listed in this comparison. Free plan details: Not stated.
- Backed by PortSwigger resources
- Supports manual and scanning work
- Requires tester skill
Acunetix is a good fit for end-to-end web security scanning. It is built to help teams take control of the security of web applications, web services and APIs. Also, agencies that build and maintain client websites can use it to check deployed applications and APIs for typical weaknesses on a repeatable basis.
Its scope is web applications and APIs, so it will not include client servers or network devices. More specifically, if you need host and network coverage, pair it with infrastructure scanning or choose a broader system. Acunetix does not show a starting price in this comparison, so check the vendor site for current pricing. As for free access: Not stated.
Downsides: Web-centric scope only.
Reasons to shortlist it: Handles web apps.
- 360 view of security posture
- Services and APIs
- Tuning needed for complicated applications
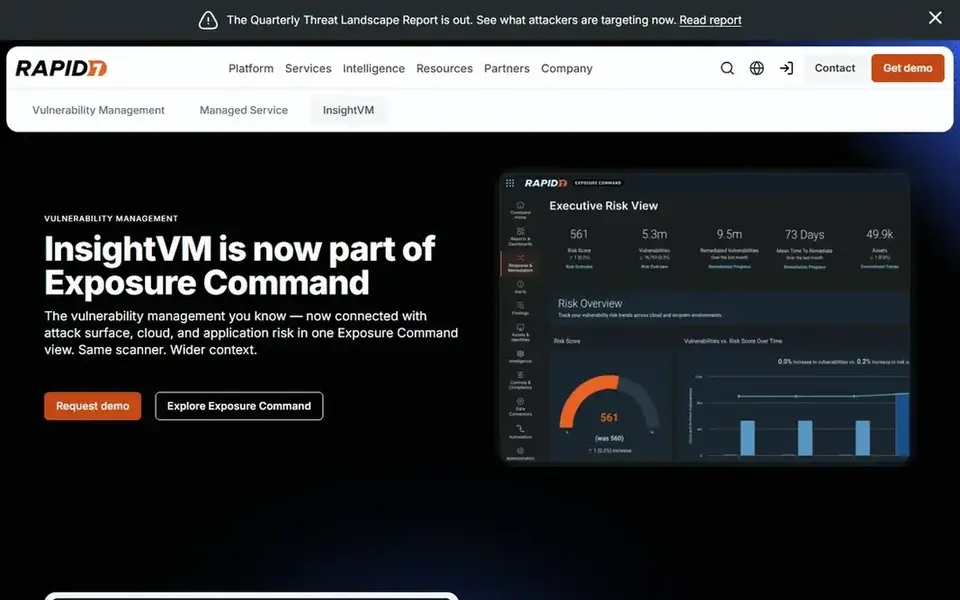
Rapid7 InsightVM is a good fit for vulnerability management with exposure context. Rapid7 InsightVM is a vulnerability management product now part of Rapid7 Exposure Command. From a buyer's view, since InsightVM is folded into a larger exposure system, teams should confirm which capabilities they actually need.
Downsides: May need onboarding effort.
Pick a focused scanner instead if your primary need is quick web application checks without a full exposure program. Beyond that, smaller agencies may find the scope broader than required. No starting price is listed for Rapid7 InsightVM here; confirm pricing on the vendor site. On free options: Not stated.
- Includes cloud and application risk context
- Demo available from vendor
- Positioned within a broader product
Where Detectify fits: external exposure checks with hacker-driven research. Detectify is an application security service built around finding what is exposed and fixing what matters before attackers do. On top of that, agencies needing full infrastructure scanning should look elsewhere.
The main drawbacks: Less depth for internal networks.
As for the details, Detectify concentrates on externally visible surfaces, so internal networks and deep host assessment fall outside its scope. The vendor describes real-world hacker research delivered at machine speed. Entry price for Detectify: €2,500 annual platform fee. Detectify offers a free plan.
- Geared toward prioritizing fixes
- Centred on finding what is exposed
- External surface focus
Choose Invicti for automatic web application and API security testing. Invicti is pitched at enterprise application security, so agencies with a handful of small sites may find it more than they need. It does not replace network or host scanning.
Beyond that, the vendor describes accurate, automatic application security testing that scales across websites, applications and APIs, and calls it a DAST-first AppSec product. Web agencies managing plenty of client sites and APIs can use it to bring automatic security testing into delivery and maintenance workflows. In daily use, choose a broader scanner when infrastructure assessment is the primary requirement instead of application testing. Entry price for Invicti: $500 per pentest. As for free access: Not stated.
The main drawbacks: Enterprise-oriented positioning.
- DAST-first application security product
- Scales across numerous sites and APIs
- Application-focused instead of network-wide
Tenable Nessus targets wide network and host vulnerability assessment. The vendor describes it as a trusted standard used by plenty of organizations. Nessus is not a DAST-first tool, so deep application logic and API testing may need a separate system.
It also takes planning to scope credentials and scan schedules across numerous clients. On top of that, for web agencies, it suits engagements where you must check client infrastructure alongside websites, for example managed hosting or retainer security reviews, and it performs well as a baseline scanner across several environments. Pricing for Tenable Nessus is not stated here, so ask the vendor for current figures. As for free access: Not stated.
Limits to weigh: Not a dedicated web app scanner.
- Well documented vendor resources
- Broad assessment coverage
- Configuration effort for large scopes
How the list was put together
We compared the tools on published pricing, free plan or trial availability, feature coverage for vulnerability scanning software for web agencies, and the limits each vendor documents. Plan names, prices and limits change often. Treat the figures here as a starting point and verify them with the vendor. Tools are placed by general fit for vulnerability scanning software for web agencies, with price clarity and free access as tie-breakers. A different team can reasonably rank them differently.
Pre-purchase checklist
- Confirm the entry price on the vendor page. For Burp Suite, Acunetix, Rapid7 InsightVM and Tenable Nessus that means a quote rather than a fixed price.
- Test the free plan from Detectify against your real workload before relying on it.
- Before choosing Burp Suite, weigh its main limit: needs tester skill.
- Ask whether Acunetix integrates with your current software, and whether that comes standard or as an add-on.
- Look at which plan of Burp Suite unlocks the features you need; entry tiers are often cut down.
Frequently asked questions
Do these tools publish their prices?
Not all of them. Burp Suite, Acunetix, Rapid7 InsightVM and Tenable Nessus publish no starting price, so expect a quote request for those. The rest, Detectify included, show a starting price, though seats and billing terms still change the final cost.
Which options for vulnerability scanning software for web agencies have a free plan?
Detectify is the only tool in this list with a free plan. Free plans usually cap users, projects or features, so check the limits on the vendor page.
Is Burp Suite the right pick for everyone comparing vulnerability scanning software for web agencies?
No single tool suits every team. Burp Suite comes first because it fits hands-on web application security testing, while Acunetix suits end-to-end web security scanning and Rapid7 InsightVM suits vulnerability management with exposure context. Match the tool to your own size, budget and workflow before deciding.
How are the tools for vulnerability scanning software for web agencies ordered?
Burp Suite sits first and Tenable Nessus last because the order follows typical fit for vulnerability scanning software for web agencies, then price clarity and free access. It is a judgement call, so read each profile for fit and limits.
Sources
See where you really rank - block by block
ProMapRanker scans Google Maps across a grid of your service area. Simple monthly plans from $19, white-label on every plan.
Start freeBrowse all guides
← 6 Best Uptime Monitoring Service for Agencies in 2026AI Knowledge Platform for IT Managers: Best Picks of 2026 →
 best ssl certificate provider for agencies
SSL Certificate Provider for Agencies: Best Picks of 2026
Shortlisting the best SSL certificate provider for agencies? 5 products compared on cost, free access and ideal buyer. Short verdicts, no fluff. Start here.
Read → best mac fleet management software for creative agencies
Mac Fleet Management Software for Creative Agencies (2026)
Searching for the best mac fleet management software for creative agencies? Here are 5 options with prices and free plans. Pros and cons for every tool.
Read → best ai enterprise content delivery network software
Best AI Enterprise Content Delivery Network Software (2026)
5 tools for the best AI enterprise content delivery network software, compared on pricing, free plans and best-fit use. Hidden costs and gaps are flagged.
Read → runpod alternatives
Best RunPod Alternatives in 2026
Looking for runpod alternatives? We compare 9 GPU cloud platforms on hourly pricing, GPU choice, serverless inference, and which workload each suits best.
Read → dropbox alternatives free
Dropbox Alternatives Free in 2026
We compared free Dropbox alternatives in 2026 with genuine free tiers, from large storage allowances to private, encrypted sync and sharing without paying.
Read → best mssp companies
Best MSSP Companies in 2026
Compare the best mssp companies and managed security service providers in 2026, with monitoring, response terms and pricing models checked for US businesses.
Read →More in IT, Cloud & Security · All guides A to Z by date · Latest guides