 ProMapRanker
Best Secure Code Review Software for Enterprise in 2026

Quality gates from IDE to CI/CD · Pricing starts at: $34 per month
Direct answer
If you need quality gates from IDE to CI/CD, SonarQube is the first tool to look at here. Listed starting prices: SonarQube from $34 per month, Snyk Code from $25 per month and GitLab Ultimate from $29 per user a month. Alternatives: Snyk Code for Securing AI-generated code and agents, and Checkmarx One for unified application security across attack surfaces. Details, prices and limits for the rest of the 5 tools are below.
ProMapRanker compared 5 tools for secure code review software for enterprise. The goal is a practical shortlist: published prices, free plan facts, best-fit use cases and honest limits for every entry.
Key takeaways
- Number one here is SonarQube, a fit for quality gates from IDE to CI/CD.
- Snyk Code has the lowest monthly starting price in this list: $25 per month.
- Checkmarx One comes with a trade-off: wide product may require onboarding effort.
- Veracode Static Analysis suits policy-driven application risk management.
Quick comparison
| Pick | Great for | Pricing starts at | Free tier | |
|---|---|---|---|---|
| SonarQube | Quality gates from IDE to CI/CD | $34 per month | Yes | Visit |
 Snyk Code | Securing AI-generated code and agents | $25 per month | Yes | Visit |
 Checkmarx One | Unified application security across attack surfaces | See website | Not stated | Visit |
 GitLab Ultimate | Security embedded in the DevSecOps product | $29 per user a month | Yes | Visit |
 Veracode Static Analysis | Policy-driven application risk management | See website | Not stated | Visit |
Every option for secure code review software for enterprise explained
Pick SonarQube if this describes you: quality gates from IDE to CI/CD. SonarQube from Sonar enforces consistent quality gates across every pull request and pipeline, from IDE to CI/CD, with automatic code review for bugs and security issues.
Where it is weaker: Rule tuning takes continuing effort.
Also, rule configuration and gate thresholds need tuning to avoid noise. Entry price for SonarQube: $34 per month. Free access exists with SonarQube.
- Coverage across IDE and pipeline
- Consistent quality gates per pull request
- Security depth varies by edition and setup
Think of Snyk Code for Securing AI-generated code and agents. That positioning suits organizations adopting AI-assisted development that want security checks close to where code is generated and committed.
Snyk Code pricing: $25 per month. You can start on Snyk Code without paying.
Trade-offs to know: Fast-moving AI features need periodic re-evaluation.
- Developer-first security system
- Agents and apps
- Security coverage relies on which products you adopt
Think of Checkmarx One for unified application security across attack surfaces. It merges hybrid scanning, AI-powered agents and unified risk intelligence across every attack surface.
Checkmarx One shows no starting price here, so confirm the cost on the vendor site. Free options: Not stated.
Honest limits: Wide product may need onboarding effort.
- AI-powered security agents
- Unified risk intelligence
- Enterprise focus can feel heavy for small teams
Pick GitLab Ultimate if this describes you: Security embedded in the DevSecOps system. Security coverage also relies on which capabilities are enabled and how pipelines are configured.
Downsides: Security depth varies by configuration.
The starting price for GitLab Ultimate: $29 per user per month. You can start on GitLab Ultimate without paying.
- Governance and context across the lifecycle
- Single product for teams and agents
- Value relies on standardizing on GitLab
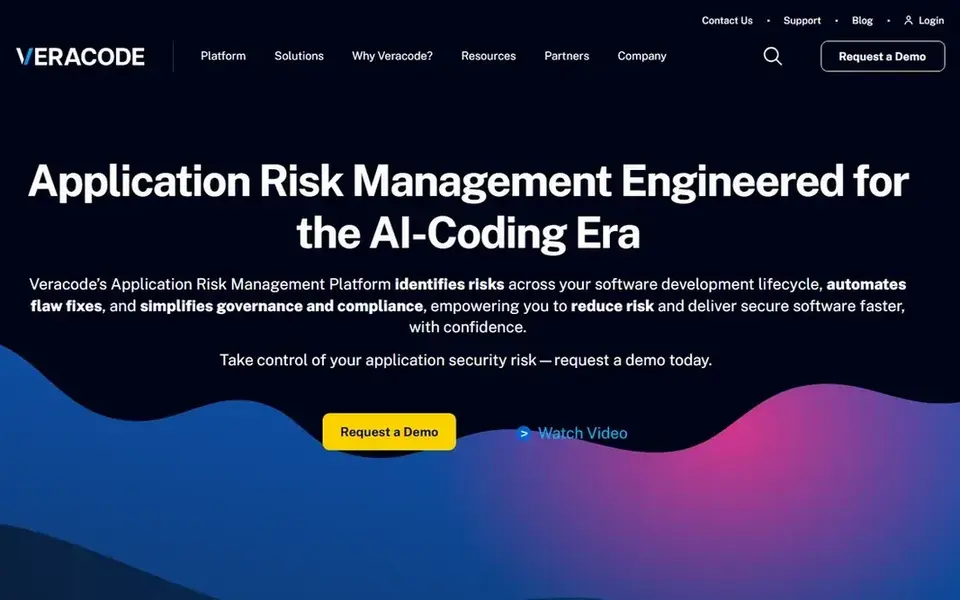
Veracode Static Analysis targets policy-driven application risk management. Veracode Static Analysis sits within the vendor's application risk management product, which the homepage frames as made for today's AI-driven world.
What to check first: Static analysis alone leaves other testing to separate tools.
Static analysis also covers only part of the testing picture, so dynamic and composition testing may need separate attention. Pricing for Veracode Static Analysis is not stated here, so ask the vendor for current figures. Free options: Not stated.
- Established static analysis offering
- Aimed at AI-driven development
- Enterprise workflows need planning
How the list was put together
Pricing pages, product documentation and feature lists were the main sources, and every entry carries at least one honest drawback. Treat prices as a snapshot: vendors change plans often, so check the vendor site for the figure that applies today. Tools are placed by general fit for secure code review software for enterprise, with price clarity and free access as tie-breakers. A different team can reasonably rank them differently.
Questions to settle before buying
- Get a written quote from Checkmarx One and Veracode Static Analysis; the list shows no starting price for them.
- Check what the free option really includes: SonarQube, Snyk Code and GitLab Ultimate offer a free plan, and usage caps differ.
- Before choosing SonarQube, weigh its main limit: Security depth varies by edition and setup.
- Confirm that Veracode Static Analysis connects to the apps your team already uses, on the plan you would actually buy.
- Make sure Snyk Code lets you export your data in a format another tool can read.
Frequently asked questions
Can I try these tools before paying?
Often, yes. SonarQube, Snyk Code and GitLab Ultimate have a free plan. Use your own data and a real task during the test, and check what the free tier or trial limits before you rely on it.
Can these tools include AI-generated code?
Multiple vendors now position around AI-assisted development, including Checkmarx One with AI-powered agents and Snyk with a focus on code AI writes and the agents it runs.
Do these tools publish their prices?
Not all of them. Checkmarx One and Veracode Static Analysis publish no starting price, so expect a quote request for those. The rest, SonarQube included, show a starting price, though seats and billing terms still change the final cost.
What is the cheapest option for secure code review software for enterprise in this list?
On published monthly entry prices, Snyk Code is the lowest here at $25 per month. Entry price is only part of the cost, because seats, add-ons and billing terms can change the total.
What should enterprises look for in secure code review software?
Prioritize language and build support, how findings reach developers, and whether the product suits your existing code hosts and pipelines. Governance and reporting matter for security programs that track remediation over time. Confirm current capabilities on vendor sites.
How are the tools for secure code review software for enterprise ordered?
The order follows typical fit for secure code review software for enterprise, with SonarQube first and Veracode Static Analysis last, then price clarity and free access. It is editorial judgement, not a score, so another team could rank the tools differently.
Sources
See where you really rank - block by block
ProMapRanker scans Google Maps across a grid of your service area. Simple monthly plans from $19, white-label on every plan.
Start freeBrowse all guides
← 6 Best Review Management Software for Enterprise in 20266 Best Self-Hosted Documentation Review platform for 2026 →
 best platforms for review & reputation control
Best Platforms for Review & Reputation Control in 2026
Comparing the best platforms for review & reputation control? 6 contenders, each with entry cost, free tier and best-fit buyer. Read the caveats before you buy.
Read → best online reputation management software for enterprise
Online Reputation Management Software for Enterprise (2026)
Shortlisting the best online reputation management software for enterprise? 6 products compared on cost, free access and ideal buyer. Straight answers.
Read → best google review management software
Google Review Management Software: Best Picks of 2026
Best google review management software in 2026: 6 tools with starting prices, free plans and limits. Plain-spoken summaries throughout. Read the profiles.
Read → best customer feedback tools
Best Customer Feedback Tools in 2026
Searching for the best customer feedback tools? We compare 8 platforms for surveys, in-app feedback, and turning customer comments into clear action today.
Read → best customer satisfaction survey tools
Best Customer Satisfaction Survey Tools in 2026
We compared the best customer satisfaction survey tools for small teams, covering CSAT, NPS, pricing, free plans, and honest trade-offs for 2026 today.
Read → best consumer insights companies
Best Consumer Insights Companies in 2026
Compare the best consumer insights companies for retail data, brand tracking, surveys, panels and market intelligence in 2026 and beyond for every budget.
Read →More in Reviews & Reputation · All guides A to Z by date · Latest guides