 ProMapRanker
Secure Code Review Software in 2026: Top 6 Compared
Direct answer
Start with Snyk if you need Securing AI-written code and agents. Listed starting prices: Snyk from $25 a month, GitLab Ultimate from $29 per user a month and Semgrep from $15 per contributor per month. If your case is different, GitLab Ultimate suits Security inside a full DevSecOps system and GitHub Advanced Security suits built-in protection for GitHub repositories. The other 3 tools in the list cover narrower or pricier cases.
This ProMapRanker guide covers 6 options for secure code review software. Each profile lists a starting price, free plan details, strengths and drawbacks, so you can drop poor fits quickly.
Key takeaways
- Snyk takes the first slot, best suited to Securing AI-written code and agents.
- Semgrep comes with a trade-off: rule quality relies on curation.
- Checkmarx One suits unified application security across attack surfaces.
- The lowest published monthly entry price here is $15 per contributor per month, from Semgrep.
Quick comparison
| Pick | Great for | Pricing starts at | Free tier | |
|---|---|---|---|---|
 Snyk | Securing AI-written code and agents | $25 a month | Yes | Visit |
 GitLab Ultimate | Security inside a full DevSecOps system | $29 per user a month | Yes | Visit |
 GitHub Advanced Security | Built-in protection for GitHub repositories | See website | Not stated | Visit |
 Semgrep | Developer-friendly SAST and secrets detection | $15 per contributor per month | Yes | Visit |
 SonarQube | Consistent quality gates in pipelines | $34 a month | Yes | Visit |
 Checkmarx One | Unified application security across attack surfaces | See website | Not stated | Visit |
Every option for secure code review software explained
For Securing AI-written code and agents, Snyk is a natural candidate. Snyk is an AI security system that secures the code AI writes, the agents it runs and the apps it builds.
The system's AI-security focus is wide, so teams should confirm which scan types match their stack before committing. If your priority is classic static review of human-written code only, a narrower tool may be more straightforward. Entry price for Snyk: $25 per month. Snyk has a free plan.
What works well: Focus on AI-written code and agents. Downsides: Coverage relies on how it is configured.
- Developer-oriented system
- Secures code
- Wide AI-security messaging may need clarification for some teams
Where GitLab Ultimate fits: Security inside a full DevSecOps system. If you only need standalone scanning, a dedicated review tool could be a lighter choice.
Entry price for GitLab Ultimate: $29 per user per month. Free access exists with GitLab Ultimate.
Drawbacks to consider: Tied to adopting the GitLab product.
- Governance and context for the whole lifecycle
- Security within the software lifecycle product
- Wide system scope can be complicated
GitHub Advanced Security is aimed squarely at built-in protection for GitHub repositories. GitHub Advanced Security supplies built-in, AI-powered protection for every repository, helping teams fix vulnerabilities and safeguard their software supply chain.
This comparison lists no price for GitHub Advanced Security; ask the vendor. Free plan details: Not stated.
Drawbacks to consider: Most natural fit for GitHub-hosted code.
- Supply chain safeguards
- AI-powered security features
- Feature depth varies by repository setup
For developer-friendly SAST and secrets detection, Semgrep is a natural candidate. It fits engineering teams that want quick, configurable scanning that developers can understand and extend.
Teams needing wide governance and risk reporting across many applications may pair it with a bigger system. The starting price for Semgrep: $15 per contributor per month. You can start on Semgrep without paying.
Drawbacks to consider: Less of a full risk-governance suite.
- Actionable findings
- SCA and secrets detection
- Rule quality relies on curation
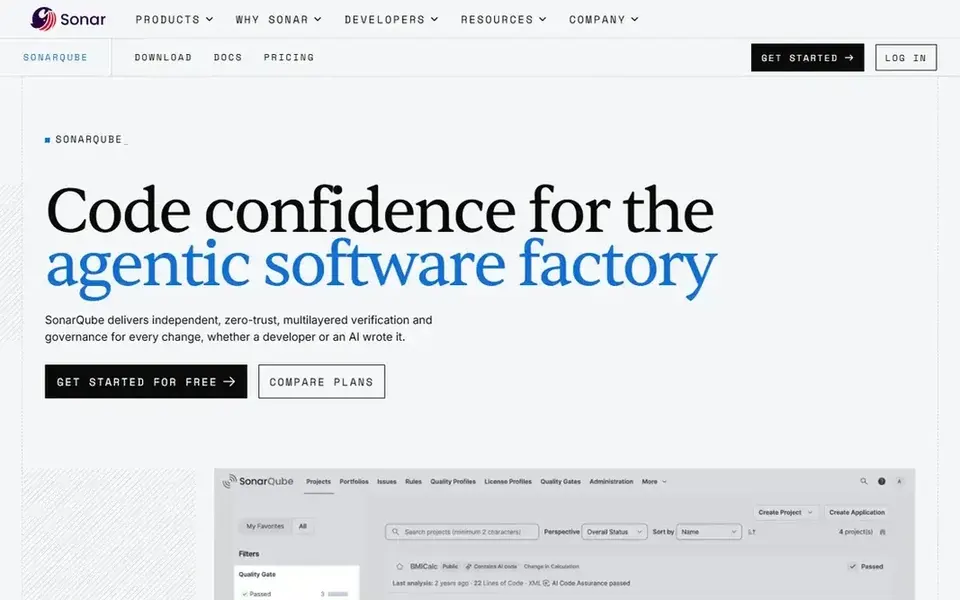
SonarQube serves consistent quality gates in pipelines. SonarQube from Sonar enforces consistent quality gates across every pull request and pipeline, from IDE to CI/CD, with automatic code review for bugs and security issues.
Downsides: Less concentrated on external dependency risk.
Its strength is first-party code review, so teams needing deep dependency or supply chain coverage may want to pair it with another tool. In practice, quality gates also need sensible tuning so they help instead of block delivery. On cost, SonarQube starts like this: $34 per month. SonarQube has a free plan.
- Quality gates across pull requests and pipelines
- Coverage from IDE to CI/CD
- Gate configuration needs tuning
Pick Checkmarx One if this describes you: unified application security across attack surfaces. Checkmarx One is an agentic application security system that merges hybrid scanning, AI-powered agents and unified risk intelligence across every attack surface.
Since the product spans numerous scanning types, initial setup and tuning can take effort, and smaller teams may find the scope broader than they need. This comparison lists no price for Checkmarx One; ask the vendor. On free options: Not stated.
The main drawbacks: Broad system can take time to configure.
- Hybrid scanning approach
- AI-powered agents
- Best value for bigger security programs
How the list was put together
The comparison looks at four things: starting price, free access, how well the feature set matches secure code review software, and the main limit of each tool. Where a price is missing, the vendor does not list one publicly or ties it to a quote. Always confirm before budgeting. The ranking is editorial: typical fit first, then clear pricing, then free access. If your needs are unusual, read the profiles rather than relying on position.
What to check before you buy
- Ask GitHub Advanced Security and Checkmarx One for a written quote, since no starting price is shown.
- Check what the free option really includes: Snyk, GitLab Ultimate, Semgrep and SonarQube offer a free plan, and usage caps differ.
- Before choosing Snyk, weigh its main limit: wide AI-security messaging may need clarification for some teams.
- Ask whether Semgrep integrates with your current software, and whether that comes standard or as an add-on.
- Verify that exporting from Checkmarx One is possible on your plan and covers all your records.
Frequently asked questions
What is the cheapest option for secure code review software in this list?
On published monthly entry prices, Semgrep is the lowest here at $15 per contributor per month. Entry price is only part of the cost, because seats, add-ons and billing terms can change the total.
Do these tools publish their prices?
Not all of them. GitHub Advanced Security and Checkmarx One publish no starting price, so expect a quote request for those. The rest, Snyk included, show a starting price, though seats and billing terms still change the final cost.
Is Snyk the right pick for everyone comparing secure code review software?
No single tool suits every team. Snyk comes first because it fits Securing AI-written code and agents, while GitLab Ultimate suits Security inside a full DevSecOps platform and GitHub Advanced Security suits built-in protection for GitHub repositories. Match the tool to your own size, budget and workflow before deciding.
Can I try these options before paying?
Often, yes. Snyk, GitLab Ultimate, Semgrep and SonarQube have a free plan. Use your own data and a real task during the test, and check what the free tier or trial limits before you rely on it.
Sources
See where you really rank - block by block
ProMapRanker scans Google Maps across a grid of your service area. Simple monthly plans from $19, white-label on every plan.
Start freeBrowse all guides
← Best Secure Code Review Software for Remote Teams in 2026Software for Getting More 5-star Reviews: Best Picks of 2026 →
 best review management software for lawyers
Review Management Software for Lawyers: Best Picks of 2026
Best review management software for lawyers: 5 contenders ranked by fit, with entry costs and free tiers. Weaknesses are named for every tool. Numbers first.
Read → best review generation software
Review Generation Software: 5 Options Compared in 2026
Weighing the best review generation software? We lined up 5 products by cost, free access and fit. Every pick includes one clear drawback. Quick to scan.
Read → best plumbing review management software
Best Plumbing Review Management Software in 2026
5 products for the best plumbing review management software, ranked by fit, with starting costs and free tiers. Honest caveats for every entry. No filler.
Read → best performance review software
Comparing 6 Performance Review Software Options in 2026
6 options for the best performance review software, with entry costs, free tiers and the buyer each one serves. Read the caveats before you buy. Numbers first.
Read → best design feedback tools
Best Design Feedback Tools in 2026
Compare the best design feedback tools for comments, annotations, versions, and approvals, with options for UI, video, print, and web teams today in 2026.
Read → best companies in the world
Best Companies in the World in 2026
A plain guide to the best companies in the world by public reputation and services, covering tech, retail, chips, finance, media and shopping for readers.
Read →More in Reviews & Reputation · All guides A to Z by date · Latest guides