 ProMapRanker
8 Companies That Offer the Best Cloud Code Security


Developer-first teams that want fast fixes · Pricing starts at: $25 per developer per month for Team
Key takeaways
- Start with the stage that creates the most risk in your stack, such as dependencies, secrets, or cloud settings, rather than buying every module at once.
- A tool that fits into pull requests and gives a clear fix will reduce risk faster than a tool that only produces long reports.
- Quote-only enterprise pricing makes budgeting hard, so ask for the pricing unit, such as developers, applications, or lines of code, before a trial ends.
- Free tiers help small teams start, but check the limits on projects, tests, and private repositories before you rely on them.
Quick comparison
| Pick | Great for | Pricing starts at | Free tier | |
|---|---|---|---|---|
| Snyk | Developer-first teams that want fast fixes | $25 per developer per month for Team | Yes, limited free tier | Visit |
 SonarQube Cloud | Teams that want quality and security gates together | From $34 per month for Team, free up to 50,000 lines of code | Yes, free tier up to 50,000 lines of code | Visit |
 Checkmarx One | Regulated enterprises with large AppSec programs | See website | No | Visit |
 Veracode | Enterprises that need attestation and audit reporting | See website | No | Visit |
 Wiz | Multi-cloud teams that want code linked to cloud risk | See website | No | Visit |
 Palo Alto Networks Prisma Cloud | Large teams already in the Palo Alto ecosystem | See website | No | Visit |
 Aqua Security | Teams focused on containers and cloud native workloads | See website | No | Visit |
 Orca Security | Cloud teams that want agentless coverage with code context | See website | No | Visit |
The best cloud code security companies
We list each option below with its official website, best fit, starting price, free plan status, strengths, and limits, followed by our notes on who it suits best.
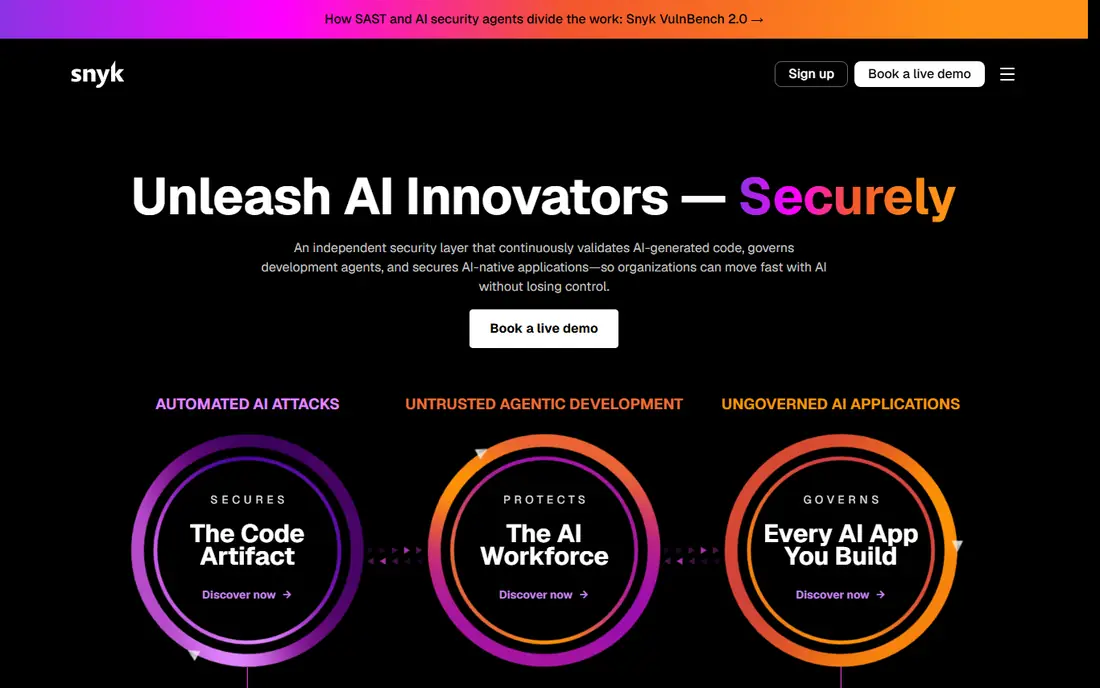
Snyk leads for teams that want security findings to arrive as fixes, not as reports to triage later. The platform covers code, dependencies, containers, and infrastructure settings, and its fix pull requests give developers a concrete next step inside the workflow they already use. We weighed that strength against price and support.
The limit is cost at scale, because per-developer pricing and enterprise tiers climb as the team grows, and some advanced features sit behind higher plans. Snyk fits a product team that ships often, values developer speed, and will judge a tool by how many findings actually get fixed. Check current terms before you commit.
- Fix pull requests, IDE and CI integration, dependency and container coverage
- Enterprise pricing is quote-only and rises fast at scale
SonarQube Cloud suits teams that want code quality and security rules enforced at the same gate. The quality gate model stops risky merges before they land, and the combination of quality and security rules helps teams that already track maintainability and test coverage. We weighed that strength against price and support.
The trade-off is pricing by lines of code, which can surprise a team with a large legacy codebase, and the deepest security rules require a paid plan. SonarQube Cloud fits a team that wants one gate for quality and security and is willing to manage lines of code as a budget input. Check current terms before you commit.
- Quality gates, pull request checks, and a free self-hosted Community Build
- Security depth is stronger on paid tiers
- Pricing scales with lines of code
Checkmarx One appeals to enterprises that need breadth and audit-ready reporting under one contract. The platform brings static, dependency, API, and container checks together, which helps a central security team set one policy across many applications and teams. We weighed that strength against price and support.
The drawback is complexity, because rollout, tuning, and false positive handling need dedicated staff, and pricing is only available through sales. Checkmarx One fits a regulated enterprise with a dedicated AppSec team and a compliance deadline that justifies a larger program. Check current terms before you commit.
- Broad SAST, SCA, API, container, and infrastructure coverage in one platform
- Quote-only pricing
- Full scans can be slow and need tuning
Veracode works for organisations that must prove security work to customers, auditors, or regulators. The policy and reporting model gives security leaders a clear record of scans, findings, and remediation progress, which matters when a customer or auditor asks for proof. We weighed that strength against price and support.
The limit is access, because there is no free scanning tier and pricing depends on application count and contract terms, so small teams face a high entry cost. Veracode fits an enterprise that treats attestation as a core requirement and has the budget for a formal, policy-led program. Check current terms before you commit.
- Policy-based scanning, attestation reporting, and binary analysis options
- Quote-only pricing
- No free scanning tier
Wiz stands out when the question is not only what is wrong in code, but what is actually exposed in the cloud. The platform links code findings to cloud context, so a team can prioritise an issue that is reachable in production over a similar issue that is not exposed. We weighed that strength against price and support.
The weakness for code-first buyers is maturity, because Wiz built its name in cloud security and its code features are still catching up to specialist code vendors. Wiz fits a multi-cloud team that already uses Wiz for cloud posture and wants code risk viewed through the same risk lens. Check current terms before you commit.
- Cloud context for code findings, agentless cloud scanning, and risk prioritisation
- Code security is newer than cloud security
- Pricing is quote-only
Palo Alto Networks Prisma Cloud
Great for: Large teams already in the Palo Alto ecosystem
Prisma Cloud suits a large team that wants cloud and code controls inside an existing Palo Alto setup. The platform covers cloud workloads, containers, and infrastructure settings with central policies, which helps a security team enforce one standard across many accounts. We weighed that strength against price and support.
The drawback is operational weight, because setup, policy tuning, and credit management need staff time, and smaller teams may find the platform larger than they need. Prisma Cloud fits an enterprise that already runs Palo Alto tools and wants a single vendor for cloud and workload protection. Check current terms before you commit.
- Broad cloud, container, and infrastructure coverage with central policy controls
- Credit-based and quote-only pricing
- Needs dedicated staff to run well
Aqua Security appeals to teams whose main risk sits in containers and Kubernetes rather than in application code alone. The container and runtime focus helps teams that ship many images and run many clusters, because image, workload, and runtime checks sit in one workflow. We weighed that strength against price and support.
The limit is code depth, because a team that needs deep static analysis may still need a specialist SAST tool alongside Aqua for full coverage. Aqua Security fits a cloud native team that prioritises container and runtime risk and wants that coverage from a specialist vendor. Check current terms before you commit.
- Container, Kubernetes, and cloud native runtime coverage
- Code coverage is narrower than specialist SAST vendors
- Pricing is quote-only
Orca Security
Great for: Cloud teams that want agentless coverage with code context
Orca Security works for teams that want broad cloud visibility without deploying agents on every workload. The agentless model gives a fast view across cloud accounts, containers, and workloads, and code findings gain context from the cloud risk around them. We weighed that strength against price and support.
The trade-off is code depth, because Orca is cloud-first, so a team with heavy custom code may need a dedicated code scanner for the deepest checks. Orca Security fits a cloud team that wants fast, agentless coverage and will pair it with a code specialist where code depth matters most. Check current terms before you commit.
- Agentless cloud scanning, container checks, and code findings in cloud context
- Code coverage is secondary to cloud coverage
- Pricing is quote-only
How we picked these
We compared official documentation, pricing pages, and app and platform listings for each vendor, and we read public reviews for scan speed, false positives, and support quality. We weighted coverage across code, dependencies, containers, and cloud settings, plus pull request integration and price transparency.
We did not test these tools on live customer systems. Our comparison rests on vendor documentation, published pricing, and public review patterns, so treat scan quality claims as vendor claims until you run a trial on your own code.
How to pick a cloud code security vendor for your team
Map your stack first. List your languages, repositories, container registry, and cloud accounts, then check each vendor against that list rather than against a generic feature table. A vendor that excels in one language may be thin in another, and cloud coverage varies widely.
Run a trial on a real repository, not a demo project. Measure how long scans take, how many findings need action, and how clear the fix guidance is. A fast scan with a vague fix still costs developer time, while a slower scan with a precise fix can save it.
Check who owns the findings after the trial. Security teams need policy, reporting, and audit trails, while developers need IDE and pull request feedback. A vendor that serves only one group will stall, because fixes live with developers and proof lives with security teams.
Confirm data handling and access rules. Ask where code is processed, how long scan data is kept, and which roles can view results. For regulated work, those answers matter as much as scan speed.
Frequently asked questions
Sources
See where you really rank - block by block
ProMapRanker scans Google Maps across a grid of your service area. Simple monthly plans from $19, white-label on every plan.
Start freeKeep reading
 worlds best local seo company
8 Worlds Best Local SEO Companies for Map Pack Growth in 2026
Compare the worlds best local seo company options for Google Business Profile work, citations, reviews, and multi-location rankings and reporting in 2026.
Read → world's best web hosting company
World's Best Web Hosting Company in 2026
Searching for the world's best web hosting company? We compared 10 hosts on price, renewal rates, speed, and support to help you choose well today in 2026.
Read → who's got the best nanny tax services
Who's Got the Best Nanny Tax Services in 2026
We answer who's got the best nanny tax services, comparing full filing, back taxes, software, and pricing so families can handle nanny taxes correctly.
Read →