 ProMapRanker
SonarQube Alternatives in 2026

Key takeaways
- The best alternatives to SonarQube depend on whether you need code quality, security scanning, or both in one platform.
- Codacy and DeepSource suit teams that want a cloud first replacement with pull request feedback and quality gates.
- Semgrep and CodeQL suit teams that want fast, customisable rules and strong open source options.
- Snyk Code, Checkmarx, and Veracode lean toward security, while Code Climate and Qodana lean toward code quality and developer workflow.
- Pricing models differ sharply, with per developer, per lines of code, and enterprise quote models, so compare cost on your team size and codebase size.
Quick comparison
| Pick | Great for | Pricing starts at | Free tier | |
|---|---|---|---|---|
 Codacy | Cloud first SonarQube replacement | See website | Yes | Visit |
 DeepSource | Automated fixes and code quality | See website | Yes | Visit |
 Semgrep | Fast custom rules and security scanning | See website | Yes | Visit |
 Snyk Code | Developer first security scanning | See website | Yes | Visit |
 Code Climate | Code quality and maintainability insight | See website | No | Visit |
 Qodana | JetBrains integrated quality checks | See website | Yes | Visit |
 Checkmarx | Enterprise application security | See website | No | Visit |
 Veracode | Enterprise security with compliance reporting | See website | No | Visit |
 Coverity | Deep static analysis for large codebases | See website | No | Visit |
The best SonarQube alternatives
We compared tools on language cover, code quality rules, security scanning, quality gates, pull request feedback, coverage tracking, deployment options, and pricing. The nine tools below all offer static analysis or code quality scanning today, and none of them is SonarQube itself.
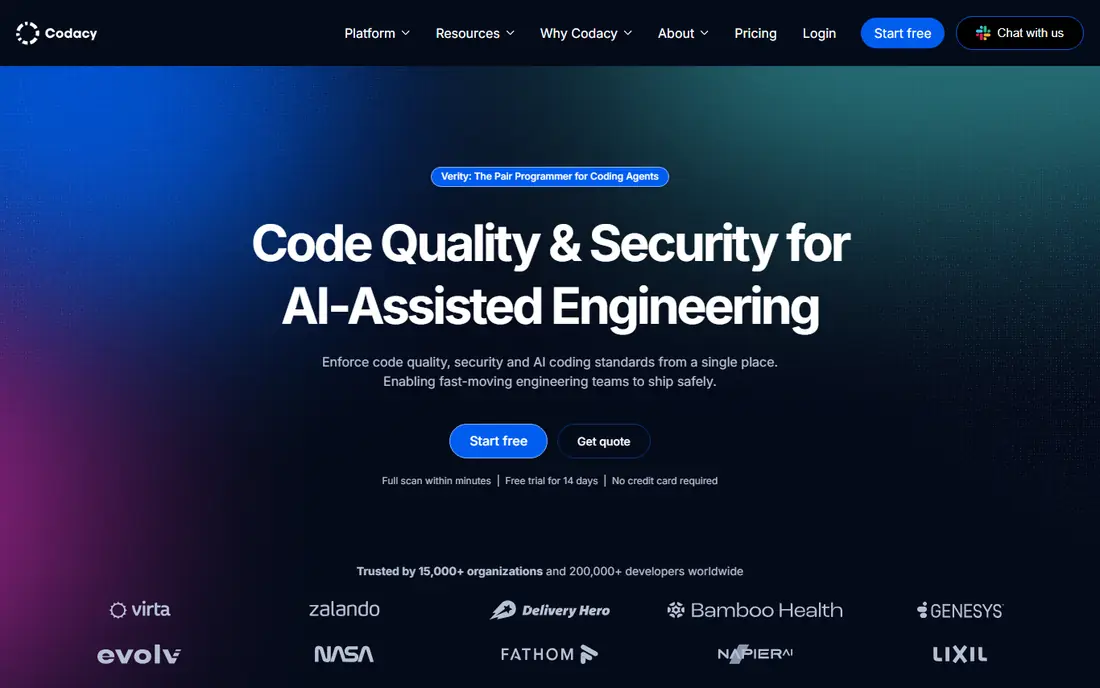
Codacy is the closest cloud first replacement for teams that want SonarQube style checks without running a server. Connect a repository, and Codacy scans pull requests, tracks coverage, and blocks merges when quality gates fail. Its language cover is broad, and its security scanning, including secrets detection, sits alongside code quality in the same platform.
The honest limit is deployment. Teams that need a fully self hosted setup may find Codacy less flexible than a self hosted SonarQube build, since self hosting is tied to higher plans. Per developer pricing also means a large team on a small codebase may pay more than a lines of code model. For cloud first teams, though, Codacy is a strong first trial.
- Cloud setup without self hosted infrastructure
- Quality gates and pull request feedback
- Broad language cover
- Self hosted option is limited to higher plans
- Per developer pricing can rise with large teams
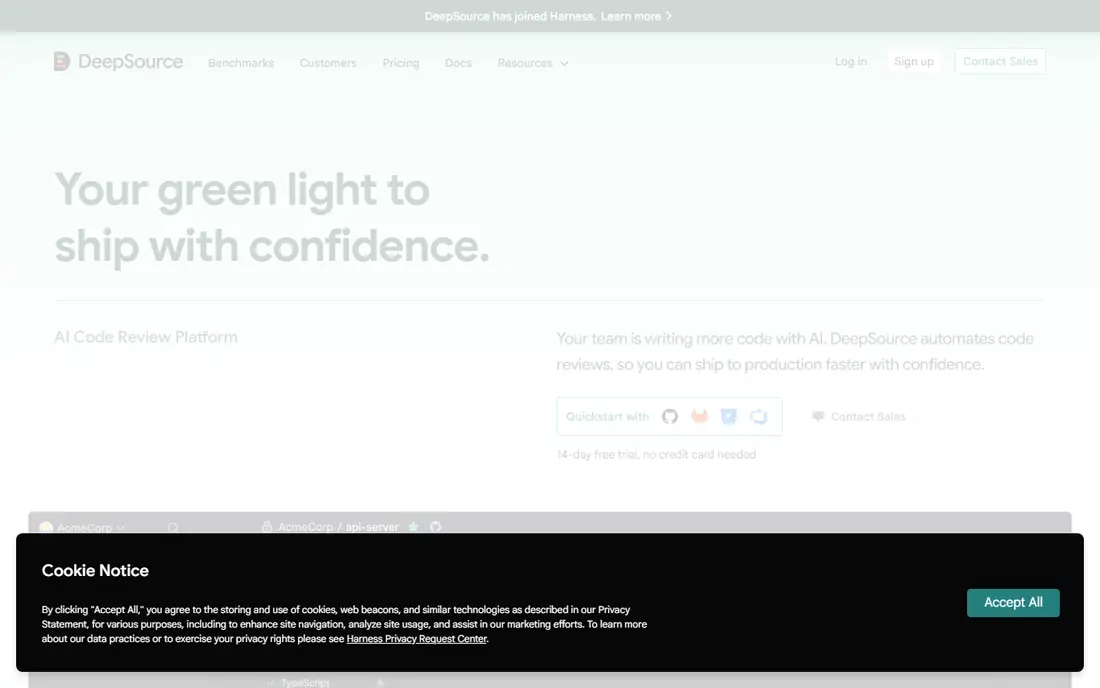
DeepSource suits teams that want fixes, not only findings. Its analyser flags code quality, security, and performance issues in pull requests, and it can open automated fixes for many common problems. That reduces the manual cleanup that often follows a new static analysis rollout, and it helps smaller teams keep quality high without a dedicated quality engineer.
The trade-off is language depth. DeepSource covers major languages well, but teams with a wide or unusual language mix should check cover before switching. Its free tier suits open source and small teams, while larger private codebases need a paid plan. For teams that value automated fixes, DeepSource is worth a direct comparison with Codacy.
- Automated fixes for common issues
- Pull request feedback
- Code metrics and security checks
- Language cover is narrower than Codacy
- Enterprise and self hosted options need a sales discussion
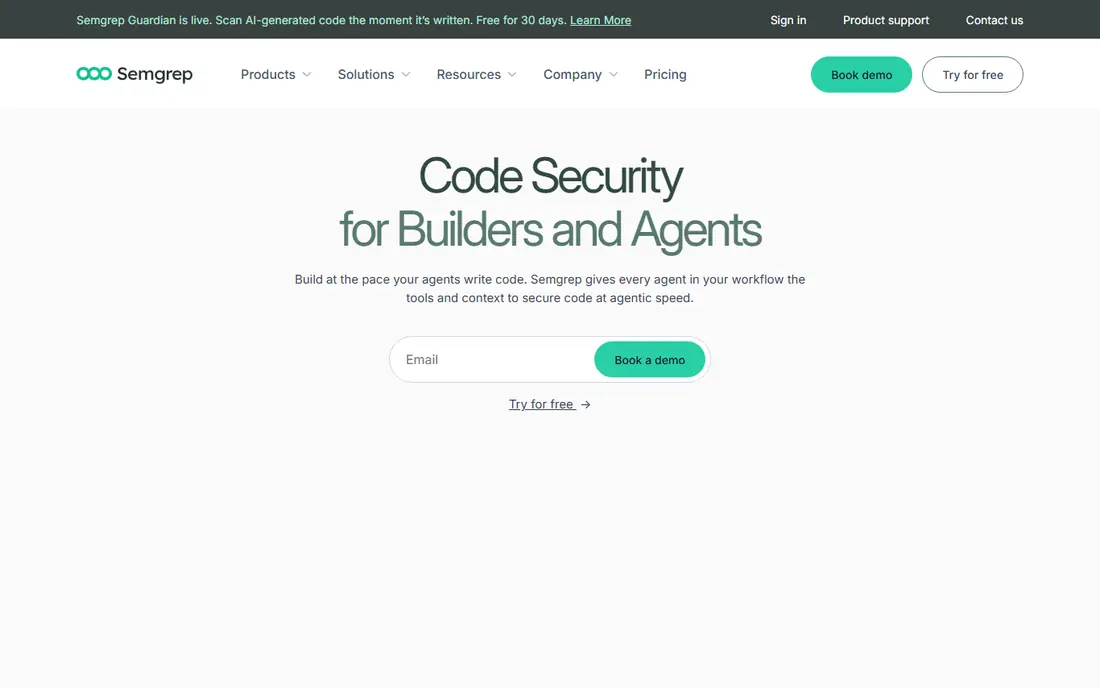
Semgrep suits teams that want control over their rules and fast feedback. Its open source core lets developers write custom rules in a readable form, and its cloud platform adds security scanning, secrets detection, and team management. Scanning is fast, which helps on large pull requests and in continuous integration pipelines where slow checks frustrate developers.
The catch is that Semgrep rewards teams willing to configure it. Out of the box quality reporting is less polished than Codacy or Code Climate, and some quality gate workflows need setup. For security focused teams and teams with custom coding standards, that control is a plus. For teams that want a ready made quality dashboard, a more opinionated tool may fit better.
- Fast scanning with custom rules
- Open source core
- Strong security and secrets scanning options
- Quality gate and reporting depth needs configuration
- Teams must write rules for some custom checks
Snyk Code suits teams whose main reason to leave SonarQube is security rather than code quality alone. It scans code for vulnerabilities, suggests fixes, and fits into editors and pull request workflows so developers see issues where they work. The wider Snyk platform adds open source dependency, container, and infrastructure scanning, which gives a fuller security view.
The honest limit is quality depth. Snyk Code is strong on security, but it does not match Codacy or Code Climate on maintainability, duplication, and technical debt reporting. Teams that need both should pair Snyk Code with a quality tool, or choose a combined platform. For security led teams, Snyk Code is a clear alternative.
- Security scanning inside developer tools
- Automated fix suggestions
- Dependency and container scanning in the wider Snyk platform
- Code quality and maintainability insight is thinner than pure quality tools
- Paid plans are needed for team features
Code Climate suits teams that care most about maintainability, duplication, and long term code health. Its quality platform rates code, tracks technical debt, and gives pull request feedback that helps reviewers focus on the riskiest changes. Coverage tracking helps teams see whether tests actually cover new code, not only whether tests pass.
The trade-off is security. Code Climate is a quality tool first, so teams that need deep security scanning will need a second tool or a different platform. Pricing can also be less transparent for larger teams. For engineering managers who want a clear maintainability view and a quality gate for merges, Code Climate remains a solid SonarQube alternative.
- Maintainability ratings and technical debt insight
- Pull request feedback
- Coverage tracking with Velocity options
- Security scanning is less central than Snyk or Semgrep
- Pricing is by quote for larger teams in some cases
Qodana suits teams that already use JetBrains IDEs, because it brings the same inspection engine into continuous integration and pull request checks. It can enforce quality gates, use a baseline to avoid flagging old code all at once, and report issues in a form JetBrains users already understand. That familiarity can speed adoption, since developers see the same checks in the editor and in the pipeline.
The limit is ecosystem fit. Teams that use Visual Studio Code or other editors can still use Qodana, but they will not get the same editor to pipeline match. Language and framework cover also follows JetBrains strengths, so check your stack before switching. For JetBrains heavy teams, Qodana is a natural SonarQube alternative.
- JetBrains inspection engine in continuous integration
- Quality gates and baseline support
- Free tier for smaller use
- Best value for JetBrains IDE users
- Non JetBrains teams may prefer a more neutral tool
Checkmarx suits large organisations that need enterprise grade application security, with policy enforcement and compliance reporting. Its static analysis covers a wide range of languages and frameworks, and its platform can combine code scanning with software composition, infrastructure, and API security in one place. That breadth helps security teams that must prove controls to auditors.
The honest limit is effort and cost. Checkmarx is an enterprise platform, with pricing by quote and setup that needs security and engineering time. Small teams will find it heavy, and teams that mainly need code quality will get more value from Codacy or Code Climate. For regulated or large scale security programs, Checkmarx is a serious alternative.
- Deep static application security testing
- Wide language and framework cover
- Compliance and policy reporting
- Enterprise pricing and setup effort
- Quality reporting is secondary to security
Veracode suits enterprises that need a full application security program, not only a code quality check. Its platform combines static analysis, dynamic testing, and software composition analysis, with policies that can block releases when risk thresholds are crossed. Compliance reporting helps teams in finance, health care, and other regulated sectors show that security checks ran and passed.
The trade-off is speed and simplicity. Veracode is heavier to set up than Codacy, DeepSource, or Semgrep, and its developer feedback loop can feel slower. Teams that want fast pull request quality checks may prefer a lighter tool, with Veracode used for release gates. For enterprise security and compliance, Veracode is a strong SonarQube alternative.
- Static, dynamic, and software composition scanning
- Policy based reporting
- Strong compliance support
- Enterprise pricing by quote
- Developer feedback can feel slower than lighter tools
Coverity, from Synopsys, suits teams with large, complex codebases, especially in C, C++, and Java, where deep static analysis matters. Its analyser is built to find serious defects with a focus on accuracy, which helps teams that cannot afford to chase many false positives. It scales to large codebases and fits into enterprise pipelines with policy controls.
The limit is accessibility. Coverity is an enterprise tool with pricing by quote, and it needs tuning by users who understand static analysis. Smaller teams and web only stacks may get faster value from Semgrep or Codacy. For safety critical, embedded, or large enterprise code, Coverity remains a respected SonarQube alternative.
- Deep static analysis with low false positive focus
- Strong C, C++, and Java support
- Scales to large codebases
- Enterprise pricing by quote
- Setup and tuning need experienced users
How we picked these
We compared official vendor pages, language cover, quality and security features, quality gate options, deployment models, and pricing structures, and we checked public reviews for patterns in false positives, setup effort, and developer feedback. We gave weight to pull request integration, clear quality gates, and realistic pricing, and we left out tools that only offer code review comments without static analysis. Where pricing was by quote or varied by team size, we wrote See website rather than publishing a single figure that would mislead.
What to check before you switch from SonarQube
Start with the job SonarQube does for you today. If it is mainly quality gates and maintainability, a quality led tool such as Codacy, Code Climate, or Qodana will fit best. If it is mainly security, a security led tool such as Semgrep, Snyk Code, Checkmarx, or Veracode will fit better. Many teams need both, so check whether one platform covers both well or whether you need two tools.
Rules, baselines, and false positives
Run a trial on your own codebase, not only on a sample project, and measure false positives on real pull requests. Check whether you can set a baseline, so old code does not block new work, and whether rules can be tuned per team or repository. A tool with many rules is less useful if developers ignore its findings because too many are noise.
Pricing on your team and codebase
Compare pricing on your actual developer count and codebase size, since per developer and per lines of code models produce very different bills. Ask about limits on scans, repositories, and pull requests, and about self hosted costs if you need that option. A short trial with real usage data will give a clearer cost picture than a headline plan price.
Frequently asked questions
What are the best alternatives to SonarQube?
Codacy and DeepSource are strong cloud first alternatives, Semgrep suits custom rules and security, and Snyk Code suits developer led security scanning. Code Climate and Qodana suit code quality, while Checkmarx, Veracode, and Coverity suit enterprise security. The best choice depends on your quality or security priority and your deployment needs.
Is there a free alternative to SonarQube?
Yes, several tools offer free tiers, including Codacy, DeepSource, Semgrep, Snyk Code, and Qodana, often for open source projects or small teams. Free tiers usually limit private repositories, users, or scans, so check limits before you rely on them for a large private codebase. Semgrep also offers an open source core you can run yourself.
Can I self host a SonarQube alternative?
Some tools offer self hosted options, but availability varies by plan. Semgrep and Coverity can run in self hosted or enterprise setups, while Codacy self hosting is tied to higher plans. If self hosting is a must, confirm it in writing, including licence terms, update effort, and support, before you choose.
Do SonarQube alternatives support quality gates?
Yes, most tools in this list support quality gates or policy checks that can block a merge or release when thresholds fail. Codacy, Qodana, Checkmarx, and Veracode offer gate or policy features, while Semgrep and Snyk Code offer policy checks in their cloud platforms. Test gate behaviour on a real pull request during a trial.
How do I migrate from SonarQube to an alternative?
Start by listing your current rules, quality gates, and coverage settings, then map them to the new tool during a trial. Run both tools in parallel on a few repositories, compare findings, and tune rules before you switch gates on. Keep a baseline for old code, so the migration does not block all new work at once.
Which SonarQube alternative is best for security?
Semgrep and Snyk Code suit developer led security scanning, while Checkmarx, Veracode, and Coverity suit enterprise security programs with compliance needs. Semgrep gives fast custom rules, Snyk Code gives developer friendly fixes, and the enterprise tools give deeper policy and compliance reporting. Match the tool to your security maturity and audit needs.
Sources
See where you really rank - block by block
ProMapRanker scans Google Maps across a grid of your service area. Simple monthly plans from $19, white-label on every plan.
Start freeKeep reading
 zoho inventory alternatives
6 Alternatives to Zoho Inventory, Compared on Price and Fit
Zoho Inventory alternatives: 6 tools compared on price, free plans and fit. Katana leads the list for manufacturers. Fit and flaws are laid out for each entry.
Read → zoho crm alternatives
Best Zoho CRM Alternatives (2026)
Need Zoho CRM alternatives? We compare 7 tools on cost, free access and who each suits. Every pick gets a straight assessment. Built for quick decisions.
Read → zelle alternatives
Best Zelle Alternatives in 2026
Compare the best Zelle alternatives for sending money to friends, paying sellers and moving funds abroad, with honest notes on fees, speed and safety in 2026.
Read →