 ProMapRanker
Best Security Compliance Tools for SaaS Companies in 2026

Key takeaways
- Vanta is our pick for SaaS teams that want broad integrations and a trust centre customers recognise.
- Drata suits teams that want a clean auditor workspace and strong monitoring.
- Secureframe suits teams planning to add more frameworks over time.
- Sprinto and Scytale suit smaller teams that want a lower entry cost for a first framework.
- Thoropass suits teams that want platform and audit help from one provider.
Quick comparison
| Pick | Great for | Pricing starts at | Free tier | |
|---|---|---|---|---|
 Vanta | Broad SaaS integrations | See website | No | Visit |
 Drata | Continuous monitoring and audits | See website | No | Visit |
 Secureframe | Teams adding frameworks later | See website | No | Visit |
 Sprinto | Budget conscious first audits | See website | No | Visit |
 Thoropass | Platform plus in-house audit | See website | No | Visit |
 Scrut Automation | Combined compliance and risk work | See website | No | Visit |
 Scytale | Guided startup compliance | See website | No | Visit |
 Hyperproof | Larger compliance programs | See website | No | Visit |
 AuditBoard | Enterprise audit and risk teams | See website | No | Visit |
The best security compliance tools for SaaS companies
We compared tools on framework coverage, integrations, evidence automation, auditor workflow, and pricing transparency. This is general information only. A tool alone does not make an organisation compliant, and audit results still depend on your controls and evidence.
Vanta is the most widely recognised name in SaaS compliance automation, and that recognition helps in sales conversations. It connects to cloud services, identity tools, and HR systems to pull evidence automatically, and it maps that evidence to frameworks such as SOC 2 and ISO 27001. The trust centre lets prospects review security documents without a long email exchange.
The main drawback is cost structure. The platform fee is only part of the total, because the audit itself is billed separately, and extra frameworks add cost. Vanta suits a SaaS team that already has enterprise prospects asking for SOC 2 and wants a platform those prospects and auditors know well. Smaller teams should get a full quote, including audit, before deciding.
- Large integration library
- Trust centre for customer security reviews
- Questionnaire automation described on its site
- Pricing is quote based
- Audit fees are separate
- Smaller teams may pay for features they do not use yet
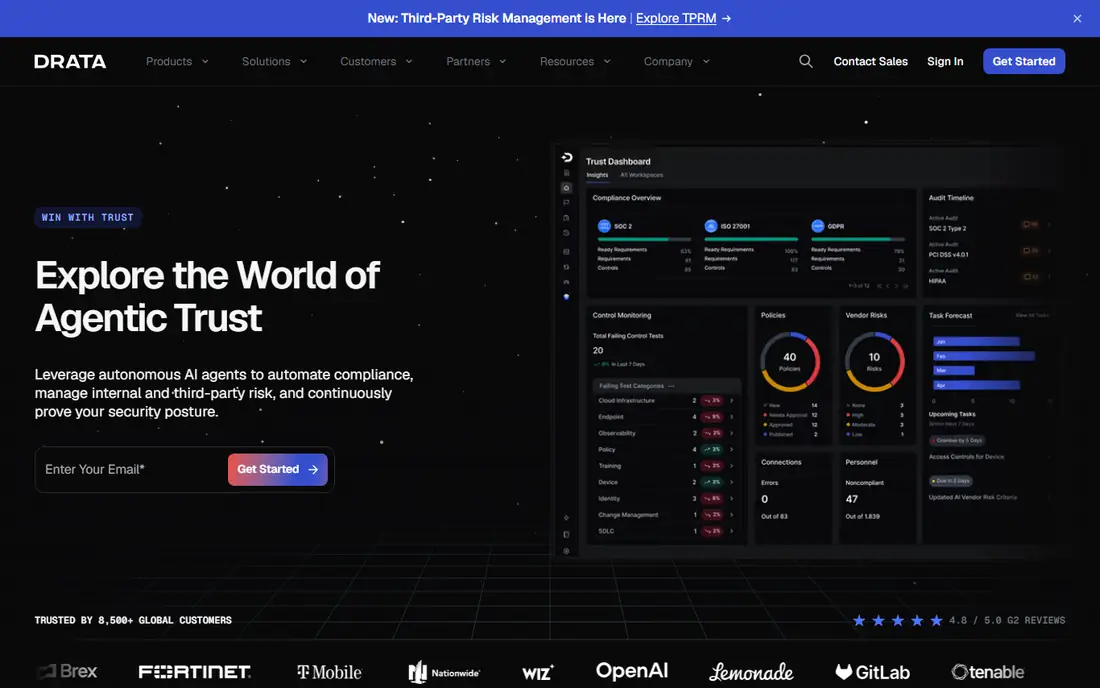
Drata focuses on keeping compliance current between audits, not just at audit time. It monitors controls continuously, flags drift, and gives auditors a structured place to review evidence. That approach reduces the scramble that often happens in the weeks before an audit, and it helps teams fix gaps early.
Drata is less attractive for a pre revenue startup that only needs a light first pass. Pricing is quote based, and the full cost includes an external audit. For a SaaS company with a security lead or a growing engineering team, Drata offers a disciplined workflow that scales as frameworks are added. Ask how many frameworks and integrations are included in the quoted tier.
- Continuous control monitoring
- Structured auditor workspace
- Broad framework library
- Quote based pricing
- Entry cost can be high for very small teams
- Audit fees are separate
Secureframe is built around the idea that a SaaS company rarely stops at one framework. It supports SOC 2, ISO 27001, HIPAA, PCI DSS, and other frameworks, with shared controls mapped across them. That shared mapping saves repeat work when a second framework is added, because evidence collected once can serve more than one standard.
The trade-off is that quotes depend on headcount, frameworks, and support level, so two similar companies can receive different prices. Advisory support is available, but check whether it is included or billed separately. Secureframe suits teams that know a second framework is coming and want to avoid rebuilding their program from scratch.
- Wide framework coverage
- Automated evidence collection
- Audit partner network
- Pricing varies by headcount and frameworks
- Advisory help may cost extra
Sprinto appeals to smaller SaaS teams because its entry pricing has often been lower than the largest rivals in marketplace listings. It automates evidence collection, tracks control status, and supports common frameworks used by SaaS vendors. For a team chasing its first SOC 2, that lower entry point can make the project feasible sooner.
Lower entry pricing does not mean lower total cost. The audit is separate, and each added framework adds cost. Sprinto still requires real internal work on policies, access reviews, and remediation. It is a good fit when budget is the main constraint and the team can handle implementation with light guidance.
- Lower entry pricing in published listings
- Broad integrations
- Guided setup for common frameworks
- Audit fees are separate
- Some advanced features sit in higher tiers
- Support depth varies by plan
Thoropass differs from most rivals because it combines compliance software with an audit practice. That combination can simplify scheduling, because the platform team and the audit team work from the same evidence. For a small SaaS team without an existing auditor relationship, that single path can remove a major source of delay.
The catch is flexibility. If you already have an auditor you trust, a bundled audit may not suit you. Thoropass is also more focused on core SaaS frameworks than on a very wide enterprise GRC catalogue. Choose it when you want one provider to carry both the platform and the audit, and confirm the audit scope in writing.
- Platform combined with audit services
- Dedicated compliance guidance
- SOC 2 focus
- Less suited to teams that already have an auditor
- Pricing is quote based
- Framework range is narrower than some rivals
Scrut Automation combines compliance automation with risk management, vendor risk, and audit preparation in one platform. That breadth helps SaaS teams that need to answer customer security questionnaires and track vendor risk as well as pass an audit. It supports common frameworks and gives smaller teams a structured path to their first report.
Brand recognition is the main weakness in the US market, where some enterprise buyers ask for a platform they already know. That does not affect audit quality, but it can mean extra explanation in security reviews. Scrut suits teams that want risk and compliance together and are comfortable with a less widely known vendor.
- Risk management alongside compliance
- Multi-framework support
- Audit support options
- Less brand recognition with US enterprise buyers
- Pricing is quote based
Scytale positions itself as a guided option for startups and mid-market SaaS companies. It pairs automation with compliance experts who help scope controls, prepare evidence, and work with auditors. That guidance matters for teams without a dedicated compliance hire, because the hardest part of a first audit is often knowing what counts as good evidence.
Costs still need careful checking. Platform, audit, and penetration testing can be separate lines, and the total depends on scope. Scytale is a strong fit when the team wants a person to guide the work, not just software to track it. Ask for a written scope that lists guidance hours, frameworks, and audit handling.
- Expert guidance included in many plans
- Multi-framework support
- Penetration testing add-ons
- Pricing is quote based
- Audit and testing fees may be separate
Hyperproof is designed for organisations that run compliance as an ongoing program across many teams. It manages controls, evidence, risks, and audit tasks in one system, with workflows that assign owners and track deadlines. That structure helps when compliance involves legal, engineering, HR, and security at the same time.
For a ten person SaaS startup, Hyperproof can feel heavy. Setup takes more effort, and pricing is quote only, which makes early comparison harder. It earns its place for mid-market and larger SaaS companies that need one system for several frameworks, internal audit, and risk tracking. Smaller teams should compare it with lighter tools before committing.
- Strong control and evidence management
- Risk and audit workflows
- Enterprise integrations
- Quote only pricing
- More complex than a first audit tool
- May be heavy for very small teams
AuditBoard is an enterprise governance, risk, and compliance platform, and its audit management roots show in its workflows. It suits SaaS companies that have grown past a single SOC 2 report and now need internal audit, risk registers, and cross team evidence in one place. Its reporting and workflow depth are stronger than most startup focused tools.
That depth comes with enterprise cost and implementation effort. AuditBoard is not the right first tool for a small team that only needs SOC 2 automation. It belongs on this list for larger SaaS companies that need compliance inside a wider risk program, with audit teams as primary users. Get an implementation estimate, not just a licence quote.
- Broad GRC platform
- Audit management strength
- Risk and compliance in one system
- Enterprise pricing and implementation
- Not built as a lightweight startup tool
How we picked these
We compared official product pages, framework lists, integration pages, and published marketplace pricing for compliance tools serving SaaS companies. We favoured tools with live SOC 2 or ISO 27001 support in October 2026, automated evidence collection, and a clear auditor workflow. We excluded tools that only sell policy templates with no monitoring or audit support.
How to choose a compliance tool without overbuying
Start with the framework your customers actually ask for. Most SaaS buyers ask for SOC 2 first, with ISO 27001 next, and HIPAA or PCI DSS only when the product touches health data or card data. Buying a platform for ten frameworks when you need one wastes budget and adds work. Confirm the framework, the audit type, and the timeline before you sign.
Separate platform cost from audit cost in every quote. Ask for the platform fee, the per framework fee, the audit estimate, and any advisory or testing fees. Then check what is included for your headcount, because many quotes change as staff numbers grow. A tool that looks cheap for twenty people can become expensive at one hundred.
Finally, check the work the tool cannot do. It can collect evidence and flag gaps, but it cannot write your access policy, approve access reviews, or fix a misconfigured cloud account. Assign an owner, set a weekly review time, and agree audit scope with your auditor early. The tool should reduce manual work, not replace accountability for controls.
Frequently asked questions
Do I need SOC 2 for a SaaS product?
Not always, but many business buyers require it before signing, especially for products that store customer data. If your prospects ask for a security review or a SOC 2 report, a compliance tool and audit become a sales requirement, not just an internal project.
How long does a first SOC 2 take?
A Type 1 report often takes eight to twelve weeks once integrations are live and policies are drafted. A Type 2 report adds an observation period, often three to twelve months, depending on scope. Remediation work between gap assessment and audit usually sets the real timeline.
Does a compliance tool replace an auditor?
No. The tool prepares evidence and tracks controls, but an independent auditor tests controls and issues the report. Budget for both, and confirm whether your vendor introduces you to auditors or expects you to bring your own.
Can one tool cover SOC 2 and ISO 27001?
Yes, most tools on this list map shared controls across frameworks, so evidence collected once can support both. That saves work, but each framework still has its own requirements and audit process. Confirm both frameworks are included in your quoted tier.
What should a small SaaS team avoid?
Avoid buying every module at the start, and avoid a tool with no named owner inside your company. Start with one framework, one audit scope, and a clear remediation list. Add frameworks and risk modules after the first audit is complete.
Sources
See where you really rank - block by block
ProMapRanker scans Google Maps across a grid of your service area. Simple monthly plans from $19, white-label on every plan.
Start freeKeep reading
 zoro.to alternatives
Best Zoro.to Alternatives in 2026
We compare the best zoro.to alternatives in 2026, listing only legal licensed anime streaming services, from Crunchyroll to free options for fans today.
Read → zip alternatives
Best Zip Alternatives in 2026
We compare the best zip alternatives for buy now, pay later in 2026, covering pay-in-4 plans, fees, spending limits, and credit reporting options today.
Read → yesware alternatives
Best Yesware Alternatives in 2026
Compare the best yesware alternatives for sales email tracking, templates, and sequences, with current pricing and honest tradeoffs for small sales teams.
Read →