 ProMapRanker
7 Bug Bounty Platforms Compared on Price and Fit

Free coordinated vulnerability disclosure · Pricing starts at: Free
Key takeaways
- Open Bug Bounty sits first on this list: free coordinated vulnerability disclosure.
- For continuous pentesting by vetted researchers, Synack is worth a look.
- What to know about HackenProof first: niche focus means less depth outside Web3.
- Expect to ask for a quote from HackenProof, Zerocopter, Bugcrowd and others; the other tools show a starting price.
- Open Bug Bounty stands alone as the one tool in this list with a free plan.
Direct answer
Our first pick is Open Bug Bounty, best for free coordinated vulnerability disclosure. For a different need, HackenProof covers Web3 and blockchain projects and Zerocopter covers EU businesses wanting disclosure-to-bounty in one shop. Prices, free plans and limits for all 7 tools follow.
Quick comparison
| Pick | Great for | Pricing starts at | Free tier | |
|---|---|---|---|---|
| Open Bug Bounty | Free coordinated vulnerability disclosure | Free | Yes | Visit |
 HackenProof | Web3 and blockchain projects | See website | No | Visit |
 Zerocopter | EU businesses wanting disclosure-to-bounty in one shop | See website | No | Visit |
 Bugcrowd | Teams wanting bounty, disclosure, and pentesting in one place | See website | No | Visit |
 Intigriti | European firms needing GDPR-compliant testing | See website | No | Visit |
 HackerOne | Large firms wanting the biggest researcher community | See website | No | Visit |
 Synack | Continuous pentesting by vetted researchers | See website | No | Visit |
7 Bug Bounty platforms in detail
ProMapRanker compared 7 Bug Bounty platforms. The goal is a practical shortlist: published prices, free plan facts, best-fit use cases and honest limits for every entry.
Open Bug Bounty works best for free coordinated vulnerability disclosure. It is a non-profit project that coordinates responsible disclosure: researchers report vulnerabilities, the project verifies them, and site operators get notified free of charge.
The main drawbacks: No bounties, triage SLAs.
From a buyer's view, the community claims over 1.5 million vulnerabilities helped fixed, mostly cross-site scripting and similar web flaws. The starting price for Open Bug Bounty: Free. A free plan is available with Open Bug Bounty.
- Fully free with no contracts or intermediaries
- ISO 29147 compatible disclosure process
- Focused chiefly on web vulnerabilities like XSS
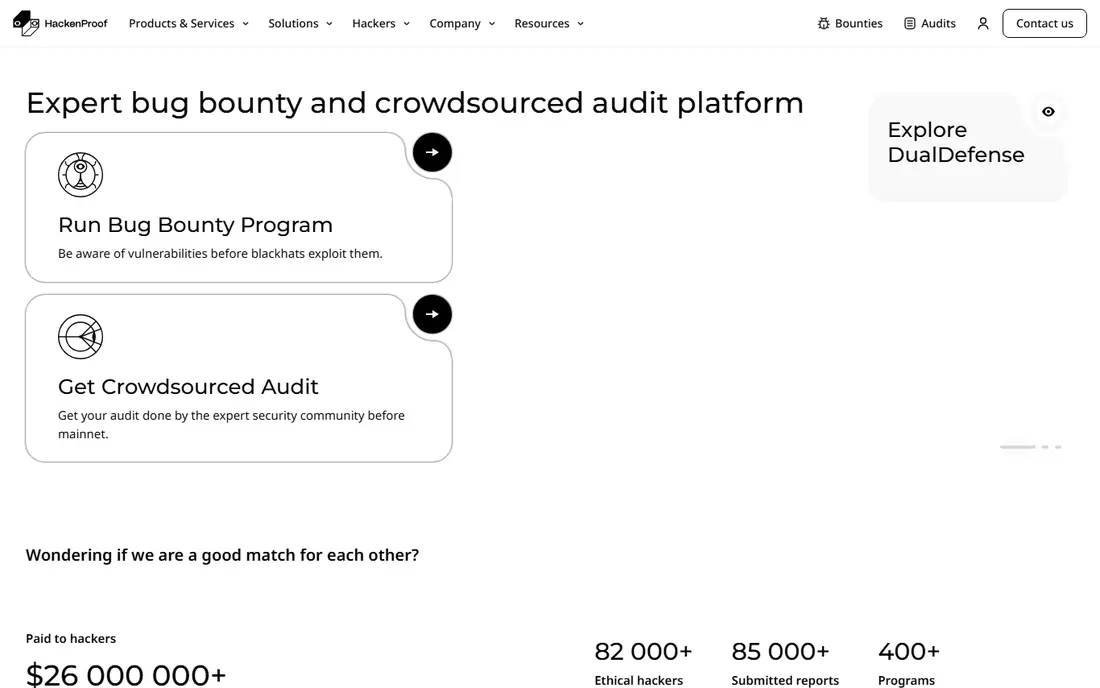
HackenProof makes the most sense for Web3 and blockchain projects. The product concentrates on crowdsourced security for blockchain protocols and smart contracts, with a researcher community that actually understands the failure modes of on-chain code. It reports tens of millions premium to hackers across hundreds of programs, with clients across major blockchain ecosystems.
As for the details, if it touches a chain, this specialization is worth more than a larger generic crowd. Generalist products can run a smart contract program, but their triage teams and researcher pools are spread thin across every technology. HackenProof does not show a starting price in this comparison, so check the vendor site for current pricing. There is no free plan with HackenProof.
Drawbacks to consider: Niche focus means less depth outside Web3.
- Deep specialization in smart contracts and blockchain
- Triage team experienced in crypto-specific vulnerabilities
- Pricing is quote-based
Think of Zerocopter for EU firms wanting disclosure-to-bounty in one shop. That ladder matters since most businesses are not ready for a public bounty on day one.
Watch-outs: Smaller international profile than the big systems.
No starting price is listed for Zerocopter here; confirm pricing on the vendor site. Zerocopter has no free plan.
- Recon and pentesting available alongside bounty
- Full journey from free disclosure channel to managed bounty
- Website and materials lean Dutch-first
Bugcrowd is aimed squarely at teams wanting bounty, disclosure, and pentesting in one place. Like HackerOne, pricing lives behind a sales call and the product assumes a serious commitment.
Honest limits: The breadth of offerings takes guidance to navigate.
Pricing for Bugcrowd is not stated here, so ask the vendor for current figures. Bugcrowd has no permanent free option.
- Researcher matching technology pairs the right hackers to your stack
- Bug bounty, VDP, pentesting
- No public pricing
Intigriti is designed for European companies needing GDPR-compliant testing. You can run bug bounties alongside managed disclosure programs and on-demand pentesting from one subscription. Intigriti is the Belgian system that turned GDPR compliance and EU data sovereignty into a competitive advantage, hosting all customer data exclusively in Europe.
Trade-offs to know: Researcher community is smaller than the two US giants.
In daily use, the system reports more than 150,000 vetted researchers and over 400 active programs, with upwards of 60 million euros premium in bounties. The community is smaller than HackerOne's, but for most businesses the quality of the first fifty researchers matters more than the size of the crowd behind them. Intigriti does not show a starting price in this comparison, so check the vendor site for current pricing. Intigriti does not include a free plan.
- Adaptable mix of bounty, VDP, pentesting
- Data hosted exclusively in Europe with capable GDPR positioning
- Pricing is quote-only
HackerOne makes the most sense for large businesses wanting the biggest researcher community. Its community of security researchers is the largest anywhere, which means niche technologies and unusual stacks still get expert eyes. From a buyer's view, pricing is not published and the engagement model assumes you can triage, remediate, and retest at pace.
Drawbacks to consider: Sheer report volume needs internal capacity to deal with.
Beyond that, a small company can absolutely run a program here. But you should go in with a tightly defined scope and a private program first. Pricing for HackerOne is not stated here, so ask the vendor for current figures. HackerOne has no permanent free option.
- Largest ethical hacker community in the industry
- AI-assisted triage and validation
- Pricing is quote-only and targeted at enterprise budgets
Pick Synack if this describes you: continuous pentesting by vetted researchers. Rather than inviting the internet to test you, it provides you continuous penetration testing from a private, vetted community of researchers, now combined with AI pentesting agents. Also, one thing to know: Synack announced a merger with NetSPI in September 2026, combining two of the biggest names in offensive security.
Drawbacks to consider: Private researcher pool means less crowd diversity than open products.
On top of that, for a mid-sized company that wants pentesting as a continuing discipline instead of an annual event, and values verified findings over raw volume, Synack is the premium choice. On top of that, the Synack product and brand continue to operate. This comparison lists no price for Synack; ask the vendor. Synack has no free tier.
- Continuous testing model rather than point-in-time
- AI-assisted pentesting with human validation
- Premium pricing pitched at bigger organizations
How we built this list
Pricing pages, product documentation and feature lists were the main sources, and every entry carries at least one honest drawback. Seat minimums, billing terms and add-ons can move the real cost, so the starting prices here are a guide and not a quote. We ordered the tools by general fit, then by how clearly pricing is shown, then by free access. A buyer with unusual needs may reorder them.
What to check before you buy
- Get a written quote from HackenProof, Zerocopter, Bugcrowd and others; the list shows no starting price for them.
- Look at the free plan from Open Bug Bounty closely: its caps decide whether it is usable for real work.
- Before choosing Open Bug Bounty, weigh its main limit: no bounties, triage SLAs, or scope control by design.
- Check whether the features you need in HackenProof sit on the entry plan or only on higher tiers.
- Ask Bugcrowd whether prices are locked for the first term and what happens at renewal.
Frequently asked questions
Is Open Bug Bounty the right pick for everyone comparing Bug Bounty platforms?
No single tool suits every team. Open Bug Bounty comes first because it fits free coordinated vulnerability disclosure, while HackenProof suits Web3 and blockchain projects and Zerocopter suits EU companies wanting disclosure-to-bounty in one shop. Match the tool to your own size, budget and workflow before deciding.
Which options for Bug Bounty platforms have a free plan?
Open Bug Bounty is the only tool in this list with a free plan. Free plans usually cap users, projects or features, so check the limits on the vendor page.
Can I try these options before paying?
Often, yes. Open Bug Bounty has a free plan. Use your own data and a real task during the test, and check what the free tier or trial limits before you rely on it.
How are the tools for Bug Bounty platforms ordered?
Open Bug Bounty sits first and Synack last because the order follows typical fit for Bug Bounty platforms, then price clarity and free access. It is a judgement call, so read each profile for fit and limits.
How much does a bug bounty program cost?
Two parts: the product fee, which vendors quote based on scope and is seldom published. The bounties you pay researchers per valid finding, which you control. Small private programs can run on modest bounty budgets, whereas public programs at large firms pay out hundreds of thousands annually.
How is a bug bounty different from a penetration test?
A pentest is a time-boxed engagement by assigned experts producing a formal report, a strong match for compliance. Pentests provide you a point-in-time assurance artifact; bounties provide you continuous coverage.
Sources
See where you really rank - block by block
ProMapRanker scans Google Maps across a grid of your service area. Simple monthly plans from $19, white-label on every plan.
Start freeKeep reading
 zoho inventory alternatives
6 Alternatives to Zoho Inventory, Compared on Price and Fit
Zoho Inventory alternatives: 6 tools compared on price, free plans and fit. Katana leads the list for manufacturers. Fit and flaws are laid out for each entry.
Read → zoho crm alternatives
Best Zoho CRM Alternatives (2026)
Need Zoho CRM alternatives? We compare 7 tools on cost, free access and who each suits. Every pick gets a straight assessment. Built for quick decisions.
Read → zelle alternatives
Best Zelle Alternatives in 2026
Compare the best Zelle alternatives for sending money to friends, paying sellers and moving funds abroad, with honest notes on fees, speed and safety in 2026.
Read →