 ProMapRanker
6 Best AI-Powered Security Analytics Platforms for 2026

Intelligent SIEM for critical threats · Pricing starts at: See website
Direct answer
For intelligent SIEM for critical threats, IBM QRadar SIEM is where this list starts. Listed starting prices: CrowdStrike Falcon LogScale from $7.99 per device a month. Exabeam Security Operations Platform fits cloud-native TDIR with AI; Microsoft Sentinel fits cloud-native SIEM with automation. The full list of 6 tools follows, with prices and free plan facts.
This ProMapRanker guide covers 6 AI-Powered security analytics platforms. Each profile lists a starting price, free plan details, strengths and drawbacks, so you can drop poor fits quickly.
Key takeaways
- The list opens with IBM QRadar SIEM, aimed at intelligent SIEM for critical threats.
- For the cheapest start, look at CrowdStrike Falcon LogScale: $7.99 per device per month.
- Microsoft Sentinel comes with a trade-off: deep integration with Microsoft ecosystem.
- Palo Alto Networks Cortex XSIAM fits AI-centric SOC transformation.
Quick comparison
| Pick | Great for | Pricing starts at | Free tier | |
|---|---|---|---|---|
| IBM QRadar SIEM | Intelligent SIEM for critical threats | See website | Not stated | Visit |
 Exabeam Security Operations Platform | Cloud-native TDIR with AI | See website | Not stated | Visit |
 Microsoft Sentinel | Cloud-native SIEM with automation | See website | Not stated | Visit |
 CrowdStrike Falcon LogScale | AI-native SOC product | $7.99 per device a month | Free trial | Visit |
 Splunk Enterprise Security | Unified TDIR with agentic AI | See website | Not stated | Visit |
 Palo Alto Networks Cortex XSIAM | AI-centric SOC transformation | See website | Not stated | Visit |
The 6 tools in detail
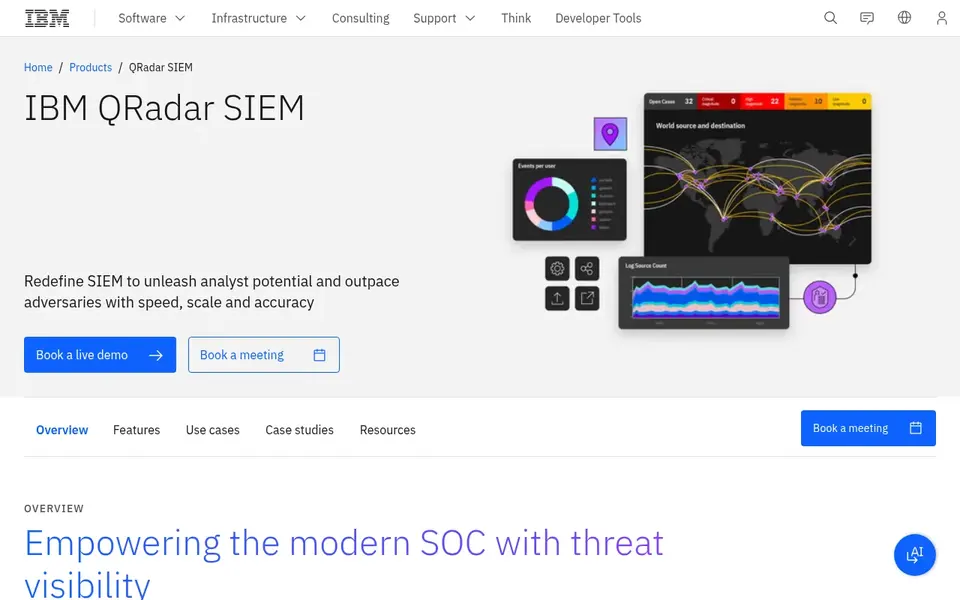
In short, IBM QRadar SIEM is for intelligent SIEM for critical threats. IBM QRadar SIEM is an intelligent security information and event management (SIEM) option that supplies actionable insight into critical threats. It is well-suited for organizations that require a proven SIEM with capable correlation and analysis capabilities, especially those already using IBM security tools.
Where it is weaker: May be less AI-centric than newer products.
As for the details, QRadar may not offer the same level of AI-native automation as some newer systems, and it can demand significant operational effort. If you seek a more AI-driven, cloud-native approach, consider Microsoft Sentinel or CrowdStrike Falcon LogScale. No starting price is listed for IBM QRadar SIEM here; confirm pricing on the vendor site. As for free access: Not stated.
- Established SIEM capabilities
- Actionable insight into threats
- Can need dedicated staff for optimal use
Pick Exabeam Security Operations Platform if this describes you: cloud-native TDIR with AI. It is made for organizations that want a modern, AI-enhanced SIEM with log management and compliance capabilities in a cloud-native architecture.
From a buyer's view, Exabeam may not have the same deep ecosystem as bigger vendors, and some enterprises may need extra integrations. Check the vendor site for Exabeam Security Operations Platform pricing; none is listed in this comparison. As for free access: Not stated.
The main drawbacks: Can be less known in some markets.
- Cloud-native product
- Simplified TDIR
- May lack some advanced features of bigger SIEMs
Pick Microsoft Sentinel if this describes you: cloud-native SIEM with automation. Sentinel's effectiveness can rely on familiarity with Microsoft's ecosystem, and some teams may find the ramp-up time steep. In practice, Microsoft Sentinel is a cloud-native SIEM designed for security operations centers (SOCs).
It spots threats quicker, automates response, and lowers SIEM costs with a data lake. Worth adding: if you need a highly customized on-premises SIEM or prefer a vendor-neutral product, consider alternatives like Splunk or IBM QRadar. Pricing for Microsoft Sentinel is not stated here, so ask the vendor for current figures. On free options: Not stated.
Where it falls short: Deep integration with Microsoft ecosystem.
- Data lake for cost efficiency
- Cloud-native SIEM
- May need tuning for non-Microsoft environments
CrowdStrike Falcon LogScale works best for AI-native SOC product. The system may offer the most value to organizations already using CrowdStrike's endpoint protection, and migrating from a legacy SIEM can be a significant undertaking.
From a buyer's view, if you need a more established SIEM with wide external integrations, IBM QRadar or Splunk might be preferable. Worth adding: CrowdStrike Falcon LogScale is positioned as an AI-native SOC product that replaces legacy SIEMs with a modern security analyst experience delivered through a single console. CrowdStrike Falcon LogScale pricing: $7.99 per device per month. Trial and free access: Free trial.
Honest limits: May be less suited for non-CrowdStrike environments.
- Replaces legacy SIEMs
- Single console for analysts
- Can need migration effort from legacy SIEMs
Where Splunk Enterprise Security fits: Unified TDIR with agentic AI. The system's breadth can introduce complexity, and smaller teams may find it resource-intensive.
Points against: Can be complicated to deploy and run.
On top of that, Splunk Enterprise Security is a unified threat detection, investigation, and response (TDIR) product that integrates SIEM, SOAR, UEBA, and agentic AI. Splunk Enterprise Security does not show a starting price in this comparison, so check the vendor site for current pricing. As for free access: Not stated.
- Integrated SIEM, SOAR, UEBA
- Simplified threat detection and response
- May need significant resources for full utilization
Palo Alto Networks Cortex XSIAM is designed for AI-centric SOC transformation. Palo Alto Networks Cortex XSIAM is a security analytics system that uses AI to centralize data, boost threat detection, and accelerate incident response across the SOC.
Check the vendor site for Palo Alto Networks Cortex XSIAM pricing; none is listed in this comparison. Free options: Not stated.
Watch-outs: May be tightly coupled with Palo Alto ecosystem.
- Accelerates incident response
- Centralizes data with AI
- Can be complicated to connect with diverse tools
What to confirm before you sign up
- Confirm the entry price on the vendor page. For IBM QRadar SIEM, Exabeam Security Operations Platform, Microsoft Sentinel and others that means a quote rather than a fixed price.
- Run a trial of CrowdStrike Falcon LogScale with real work before paying for a year; your own workflow is the best test.
- Before choosing IBM QRadar SIEM, weigh its main limit: may be less AI-centric than newer systems.
- A short pilot of CrowdStrike Falcon LogScale with your real workflow tells you more than a feature table.
- Confirm you can export your data from Microsoft Sentinel, so leaving later does not mean losing records.
Frequently asked questions
Can I try these options before paying?
Often, yes. CrowdStrike Falcon LogScale offers a free trial. Use your own data and a real task during the test, and check what the free tier or trial limits before you rely on it.
What is the cheapest option for AI-Powered security analytics platforms in this list?
On published monthly entry prices, CrowdStrike Falcon LogScale is the lowest here at $7.99 per device per month. Entry price is only part of the cost, because seats, add-ons and billing terms can change the total. For the full picture, the cards above cover all 6 entries of this AI-Powered security analytics platforms list, including price, free plan and limits.
Does any tool for AI-Powered security analytics platforms here have a free plan?
No tool in this list, IBM QRadar SIEM and Palo Alto Networks Cortex XSIAM included, has a permanent free plan. CrowdStrike Falcon LogScale offer a trial. Trials and quotes are the usual route, so plan a short evaluation period.
Do these tools publish their prices?
Not all of them. IBM QRadar SIEM, Exabeam Security Operations Platform, Microsoft Sentinel and others publish no starting price, so expect a quote request for those. The rest, CrowdStrike Falcon LogScale included, show a starting price, though seats and billing terms still change the final cost.
What is an AI-powered security analytics platform?
An AI-powered security analytics system uses artificial intelligence and machine learning to enhance threat detection, investigation, and response. It generally merges SIEM, UEBA, SOAR, and other capabilities to help security teams identify and address threats more efficiently.
How do I choose between Microsoft Sentinel and Splunk Enterprise Security?
Microsoft Sentinel is a cloud-native SIEM with solid automation and a data lake for cost efficiency, well suited to organizations seeking a scalable, Microsoft-integrated option.
Sources
- IBM QRadar SIEM: ibm.com/products/qradar-siem
- Exabeam Security Operations Platform: exabeam.com
- Microsoft Sentinel: microsoft.com/en-us/security/business/siem-and-xdr/microsoft-sentinel
- CrowdStrike Falcon LogScale: crowdstrike.com/platform/next-gen-siem
- Splunk Enterprise Security: splunk.com/en_us/products/enterprise-security.html
- Palo Alto Networks Cortex XSIAM: paloaltonetworks.com/cortex/cortex-xsiam
See where you really rank - block by block
ProMapRanker scans Google Maps across a grid of your service area. Simple monthly plans from $19, white-label on every plan.
Start freeBrowse all guides
← AI Mobile Device Management Software in 2026: Top 6 ComparedBest AI Vulnerability Management Software (2026) →
 best ai iot security solutions
5 Best AI IoT Security Solutions for 2026
5 best AI IoT security solutions, with entry costs, free tiers and the buyer each one serves. Strengths and weak spots are spelled out. Updated November 2026.
Read → best ai dns security solutions
Top 6 AI DNS Security Solutions, Compared on Price (2026)
Best AI DNS security solutions in 2026: 6 contenders with entry costs and free tiers. The weak spots sit next to the strengths. Current for November 2026.
Read → best ai data center security solutions
Best AI Data Center Security Solutions (2026)
Best AI data center security solutions: 6 tools compared on price, free plans and fit. The weak spots sit next to the strengths. Skim the table first.
Read → best cybersecurity platforms
6 Top Cybersecurity Platforms Compared (2026)
Best cybersecurity platforms: 6 tools compared on price, free plans and fit. We put Wiz first for cloud security posture. Real limits included. Facts only.
Read → xeox rmm alternatives
Best Xeox RMM Alternatives in 2026
We compared 9 xeox rmm alternatives for MSPs and IT teams, with patching, remote access, automation and pricing models that suit different team sizes.
Read → best owner operator companies
Best Owner Operator Companies in 2026
Compare the best owner operator companies in 2026, with load choice, dispatch freedom, freight types and support programs explained clearly for drivers.
Read →More in IT, Cloud & Security · All guides A to Z by date · Latest guides